privacy

Kenya’s internet metering bill raises privacy and affordability concerns | Internet News

Nairobi, Kenya – A proposed law requiring internet service providers in Kenya to monitor subscribers’ data consumption and introduce identifiable meter numbers has drawn opposition from industry and civil society groups, amid concerns about affordability, privacy and the handling of personal information.

The Kenya Information and Communications (Amendment) Bill, 2025, sponsored by Aldai MP Marianne Jebet Kitany, seeks to make consumption-based internet billing mandatory. It would require providers to assign each customer a unique meter number, monitor usage, convert it into readable details and issue invoices based on consumption.

The Bill’s stated objective is to protect consumers from unfair billing and ensure they pay for the internet they use. But the Communications Authority of Kenya (CA), telecommunications companies and civil society organisations have questioned whether mandatory metering is necessary and whether the proposed framework provides adequate safeguards for subscribers’ information.

The debate has intensified as the National Assembly’s Departmental Committee on Communication, Information and Innovation considers the legislation. The regulator has urged legislators not to make metered billing compulsory, while Telkom Kenya has warned of potential consequences for privacy, affordability and investment.

Privacy at risk

The Bill would require internet service providers to operate systems that monitor customer usage, convert consumption into readable details and generate invoices. Providers would also have to submit information about their billing systems, including subscriber meter numbers, to the regulator at least once every financial year.

The proposed provisions do not expressly require providers to record the content of private messages or the websites subscribers visit. However, civil society organisations have questioned what usage information would be collected and how identifiable records would be stored, accessed and shared.

The International Commission of Jurists (ICJ) Kenya has questioned the necessity of mandatory metering, arguing that the regulator already has powers to address billing complaints and protect consumers.

Demas Kiprono of ICJ Kenya has argued that the proposed system raises questions about whether the collection of identifiable usage information is necessary and proportionate to the Bill’s stated consumer-protection objective.

The concerns relate to the potential consequences of linking individual subscribers to records of their internet use. Critics say the legislation should specify who could access such information, how long it could be retained and the circumstances in which it could be disclosed.

Kenya’s Data Protection Act, 2019, already provides a framework for processing personal information. Opponents of the Bill say Parliament should make clear how those protections would apply to the proposed metering system.

The Mokaya case

Questions about telecommunications data have also featured in court proceedings involving university student David Ooga Mokaya.

He was arrested in November 2024 over a social media post concerning President William Ruto and charged with publishing false information. On February 19 this year, Senior Principal Magistrate Caroline Nyaguthii acquitted him under Section 215 of the Criminal Procedure Code, finding that the prosecution had not proved its case beyond reasonable doubt.

Kenya’s proposed internet metering law raises concerns over privacy, affordability and digital rights.
Kenya’s internet billing proposal faces backlash over data privacy and potential costs to consumers [File: Al Jazeera]

After his acquittal, Mokaya filed a petition at the High Court seeking protection of his personal information. He argued that information, including call data records, subscriber details, location data and metadata had been supplied to investigators without his consent. The allegations form part of the separate civil proceedings and should not be treated as a final judicial finding.

On February 25, Justice Bahati Mwamuye issued interim conservatory orders restraining the respondents and interested parties from transferring, sharing or disclosing Mokaya’s personal data without his written consent, a valid court order or an express provision of written law permitting disclosure.

The orders were issued pending further proceedings in the case. They do not establish that the proposed internet metering system would be used for surveillance. They do, however, illustrate the legal questions that can arise over the collection and disclosure of telecoms data.

The cost of data

Privacy is not the only concern. Mandatory consumption-based billing could also affect how households and businesses budget for connectivity.

In a submission to parliament on November 3, the Communications Authority cautioned against making metered billing compulsory across the sector. It said the approach could have unintended consequences for affordability, digital inclusion and consumer choice, particularly among low-income households, students, small businesses and communities in underserved areas.

The regulator noted that background applications, software updates, streaming and cloud services can consume data without users closely monitoring their usage.

Instead of prescribing one billing model, the Authority proposed usage alerts when subscribers reach 50, 80 and 100 percent of their data allowance, free real-time usage dashboards and monthly spending caps. It also recommended independent certification and periodic audits of metering systems, clearer itemised bills and stronger procedures for resolving billing disputes.

The Authority’s position is that consumer protection can be strengthened through regulations and licensing requirements without requiring every provider to adopt consumption-based pricing.

The financial impact of a change would depend on providers’ pricing and individual patterns of internet use. Customers who consume relatively little data could benefit from paying according to usage, while those who rely on large or continuous data allowances could face different costs. The Bill does not set the retail prices providers would charge.

Business concerns

Telecommunications companies have questioned whether the proposed changes could impose additional costs on providers and affect investment in broadband services.

Telkom Kenya Chief Executive Officer Mugo Kibati told the parliamentary committee on November 10 that mobile internet accounts for about 96 percent of data subscriptions and is already billed by volume. The proposed changes would therefore mainly affect fixed broadband services, which account for the remaining share, he said.

According to the Kenya News Agency’s report of the hearing, Telkom argued that a uniform metering framework could increase compliance costs and create risks for subscriber privacy and investment.

The company proposed that providers disclose their billing models, charges and fair-use policies before customers subscribe. It also called for free access to consumption information, itemised bills on request, effective dispute-resolution mechanisms and independent audits where billing accuracy is questioned.

Telkom further urged legislators to protect unlimited and speed-based internet packages, allow providers at least 18 months to comply with any new requirements and require aggregated rather than individually identifiable subscriber information to be submitted to the regulator.

Carole Kairuki, chief executive of the Kenya Private Sector Alliance, also raised concerns about the potential effect of mandatory metering on businesses. In an interview with Al Jazeera, she said changes to internet billing could increase compliance costs and make connectivity expenses less predictable for businesses, particularly smaller enterprises.

A wider debate

The Bill’s memorandum says the proposed amendments are intended to protect consumers from exploitation and secure their economic interests under Article 46 of the Constitution. It also states that the legislation does not limit fundamental rights and freedoms.

The disagreement is over whether mandatory metering is the most effective way to achieve that objective and whether the proposed provisions offer sufficient protection for subscribers’ information.

The debate comes amid wider public scrutiny of digital rights and the handling of online activity in Kenya, particularly following the 2024 protests against the Finance Bill. Kelvin Kubai, an Advocate of the High Court of Kenya, told Al Jazeera that internet access is important to young people’s civic participation and their ability to hold public officials accountable. He argued that any new regulatory framework should take those uses into account.

Parliament must weigh the Bill’s consumer-protection objective against concerns raised by the regulator, internet providers and civil society groups. The Communications Authority has proposed greater billing transparency, usage alerts and independent audits as alternatives to compulsory consumption-based billing.

Telkom CEO Kibati warned politicians against imposing obligations that could undermine a developing sector.

“Sometimes you can go overboard in trying to protect consumers that you actually kill a nascent, growing sector,” he told the parliamentary committee.
Source link

FBI national crime database suffers suspected breach: Reports | Technology News

The reported hacking is the latest in ​a string of breaches and outages affecting the US government.

The FBI’s national criminal database has suffered a suspected breach, according to multiple US media reports.

President Donald Trump, who has repeatedly downplayed breaches affecting departments within his administration, appeared to confirm the FBI hacking during a television interview on Saturday.

Recommended Stories

list of 3 itemsend of list

“Well, we just heard about it, and I will say that it’s not good. I don’t like that,” Trump told Fox News.

On Friday, CNN and NBC reported that the National Crime Information Center (NCIC), which is used by law enforcement agencies across the United States to share information on criminal warrants and background checks, was compromised, citing two people who had been briefed on the matter.

The reported hacking, which would be the second to hit the bureau this year, is the latest in a string of US government breaches and outages that have alarmed officials over the past week.

In a separate incident, NBC reported an apparent cyberattack against the US Department of Agriculture.

The FBI and USDA did not immediately return Al Jazeera’s request for comment.

In the interview on Saturday, Trump suggested the hack of the FBI’s crucial database could be viewed with “a positive spin”.

“Maybe we’ll learn things that we would have never learned otherwise. You had the Russia, Russia, Russia hoax. You had all these other hoaxes,” he said in an apparent reference to his discontent with the FBI’s investigation into Russian interference in the 2016 US election.

In September, the FBI said it was investigating an apparent breach by a cyber group that claimed it had stolen sensitive information on the bureau’s 38,000 employees.

Additionally, in March, the agency said it had been investigating “suspicious activities” on some of its internal systems, The Associated Press news agency reported.

FBI Director Kash Patel, who has not publicly commented on the most recent hacking, was not present for a Wednesday hearing at the US Capitol to examine threats against the US. Patel’s deputy, Christopher Raia, attended in his place, joining US Department of Homeland Security Secretary Markwayne Mullin and US Director of National Intelligence Jay Clayton.

Source link

Canada’s beloved Tim Hortons brews ire over ‘excessive’ Israeli data deal | Business and Economy

When Canadians order their morning cup of joe using the coffeehouse chain Tim Hortons app, coffee may not be the only thing being delivered. Users’ sensitive personal data could also be travelling across the world – to an Israeli cybertech company.

The beloved nationwide chain has found itself at the centre of an angry backlash over consumer privacy and its ties to Forter, the Israeli firm.

Recommended Stories

list of 3 itemsend of list

On Tuesday, Canadians for Justice and Peace in the Middle East (CPJME) revealed that the Tim Hortons app has been sending “sensitive user data” to Forter. Al Jazeera has independently confirmed that the app does share user data with Forter.

CPJME also raised concerns about Forter’s founders’ links to an Israeli military intelligence unit accused of mass surveillance of Palestinians, as well as the unit’s reported association with Lavender, an artificial intelligence (AI) system used to generate lists of Palestinians to be targeted during Israel’s genocidal war on Gaza.

The group’s findings build on an investigation by Canadian broadcaster CBC reported last week, examining the data-sharing practices of some of the country’s most popular apps. But the investigation did not identify which company was receiving Tim Hortons users’ data or disclose where it was based.

Neither Tim Hortons nor its parent company, Restaurant Brands International (RBI), had responded to Al Jazeera’s queries by the time of publication. Forter had also not responded to Al Jazeera’s queries.

Tim Hortons told CBC that the data-sharing arrangement is a fraud-prevention measure. However, experts have described the extent of the data collected as overly intrusive.

“The collection occurs prior to consent, and in my view is excessive,” Joel Reardon, a computer science professor at the University of Calgary whose research underpinned the CBC investigation, told Al Jazeera.

CPJME, meanwhile, warned that the practice could expose consumers to privacy risks that extend far beyond the original purpose of fraud prevention.

“What concerns us is that there is this massive … digital footprint being built of people through these apps, seemingly without their knowledge, in the name of preventing fraud, and that data is flowing to an Israeli cybertech company whose operations … [are] opaque to us and [who] have concerning ties,” Jason Toney, CJPME’s director of media advocacy, told Al Jazeera.

epa04369833 A general view of a Tim Hortons restaurant in Toronto, Canada, 26 August 2014. Burger King is buying the Canadian doughnut chain Tim Hortons for 11 billion US dollars, the US company said 26 August. Burger King said the two companies would continue to operate under their own brands and have separate management. The two firms will have 18,000 restaurants in 100 countries and an annual turnover of about 23 billion dollars. EPA/WARREN TODA
A Tim Hortons outlet in Toronto, Canada [EPA]

During its investigation, CBC found that the apps it examined, including Tim Hortons’, disclose that they collect or share certain data. However, experts questioned whether the amount of information gathered was proportionate to the simple act of buying a cup of coffee.

CBC found that the app appeared to send data to the third-party company right when it launches. This data includes unique identifiers, sensor details and the names of nearby Wi-Fi networks, which Reardon said can be used to determine a person’s location.

“I’m usually troubled by the precise ongoing location data collection because that can reveal a great deal of information about an individual,” said Reardon.

He explained that Forter gathers enough information from the Tim Hortons app to create a digital fingerprint for each device, so it can be identified in the future.

That is concerning for OpenMedia, a Canadian organisation advocating for digital rights, privacy and consumer protection.

“People open the Tim Hortons app to order a coffee, not have their data, including location indicators, exported to foreign companies,” its executive director, Matt Hatfield, told Al Jazeera.

But he said Tim Hortons is not unusual in doing this. “Many companies quietly pass data to a long chain of vendors that customers have never heard of and never chose.”

“We effectively create these chains of trust that our data is handled appropriately – where any company along the chain can breach and abuse our data,” Hatfield said.

Tim Hortons told CBC that the third party it works with – Forter – is not allowed to sell the data it collects through its app and that the coffee chain itself does not sell users’ personal information.

But Reardon said effective fraud prevention can be carried out without collecting data giving users’ precise locations.

“It is useful to be clear if Tim Hortons is talking about protecting [themselves] from fraud, or if they [are] protecting the users,” the researcher added.

Forter’s founders have previously told media that the data it receives is used to protect “wealthy corporations” from fraudulent activity, Toney noted. “If a consumer’s credit card is fraudulently used, for example, to purchase something online, it’s usually the wealthy corporations that are on the hook for reimbursing that funding,” he explained.

“So they use Forter to avoid having to take on those costs … It’s not really about protecting ordinary consumers, at least that’s not how they have framed it publicly in the past.”

Beyond the companies handling the data, there are questions about whether consumers understand what they are agreeing to. The Tim Hortons app, in its user policies, states that when customers use it, they agree to its terms.

“Research shows that consumers are frequently unaware of the particulars they consent to when accepting a privacy policy,” Johanna Gunawan, an assistant professor of computer science and law at Maastricht University, told Al Jazeera.

Such policies are lengthy and often not conveyed in plain language, she said.

“The cognitive load to understand the full privacy implications of acceptance is frequently imbalanced against the relative ease or speed of providing agreement,” explained Gunawan.

Questions about the app’s data practices do not end with what information is collected or whether users consent to sharing it. They also extend to the company receiving that data.

Forter’s founders – Michael Reitblat, Liron Damri and Alon Shemesh – are all alumni of the Israeli military’s Unit 8200, its signals intelligence and cyberwarfare division, The Times of Israel has reported. The company’s technology is enhanced by Israeli military intelligence, The Jerusalem Post reported in 2018.

Last year, Microsoft barred the Israeli military from some of its services following an investigation which found that Unit 8200 used its Azure cloud computing platform to store phone call data obtained through mass surveillance of Palestinians in Gaza and the occupied West Bank.

The division has also been associated with Lavender, the AI technology that Israel has created to target Palestinians during its genocidal war on Gaza.

While the ties are “concerning”, said CPJME’s Toney, he cautioned against speculating whether Forter uses data collected through the Tim Hortons app in a “nefarious” manner. There is no evidence of this, and he added that the Israeli firm appears to be well established.

On its website, Forter says it works on fraud prevention for many high-profile companies, ranging from eBay to Shein, Reebok and LG Electronics.

Al Jazeera was not able to confirm whether Forter still uses Israeli military intelligence or whether any data it holds is accessible to the Israeli government or military agencies.

Outdated privacy laws

This is not the first time Tim Hortons has landed in hot water over its handling of user data.

In 2022, Canadian federal and provincial privacy commissioners found that the company’s app had illegally tracked users’ locations through a third-party provider, even when the app was closed.

Tim Hortons faced no fines then because Canada’s privacy regulator cannot issue them, said OpenMedia’s Hatfield.

He said Canada’s privacy laws are insufficient and outdated.

“Our federal private-sector privacy law, PIPEDA, is more than 25 years old. Under it, a company can send your data to a service provider without asking you, as long as it says it remains ‘accountable’ for that data,” said Hatfield, referring to Canada’s Personal Information Protection and Electronic Documents Act.

“In practice, Canadians often can’t find out who receives their data, which country it ends up in, or which foreign laws or governments might be able to reach it.”

He said companies should be telling their customers this directly and respecting their stated preferences for how their data is used.

Bill C-36, the government’s new proposed privacy legislation introduced in June this year, meanwhile, “would only partially help”, said the digital rights advocate.

“It would require a privacy impact assessment before data leaves Canada, and it would introduce real financial penalties,” said Hatfield. “But it still lets companies hand data to service providers without consent, and those providers would only be directly bound by its security and breach-reporting rules.”

More worryingly, he added, the bill places privacy enforcement under a new regulator, which will be required to consider factors beyond privacy, including Canada’s trade agreements, economic growth and the broader public interest, before launching an investigation into a privacy violation.

“In practice, this may mean that while privacy violations may be more clearly illegal once C-36 passes, the Canadian government could pressure the regulator to ignore violations associated with close trade partners,” said Hatfield.

Despite the results of its last investigation, CPJME is now calling for another inquiry by the Office of the Privacy Commissioner of Canada to look into the handling of consumer data by Tim Hortons, said Toney.

Al Jazeera contacted the privacy commissioner’s office about this but did not receive a response.

‘Off the hook’

Toney’s organisation has also filed a complaint with the CBC’s ombudsperson, citing violations in journalistic standards and practices for failing to disclose Forter’s identity in its own investigation.

“CBC’s reporting obscures the true scale of the privacy risk Tim Hortons has exposed its users to. CBC is letting Tim Hortons and Forter off the hook. Canadians deserve to understand the truth,” said Toney.

Maastricht University’s Gunawan said she also believes companies should take responsibility for the privacy and security practices of third-party technology providers.

“That’s simple transparency and due diligence,” she said.

Hatfield said: “Questions about a vendor’s ties to any foreign military or intelligence service are legitimate and deserve clear answers. The same standard should apply whether the vendor is American, Chinese, Israeli or Canadian.”

At minimum, said Hatfield, Tim Hortons should publicly name every third party that receives data from its app and explain why it sends that data. The company should also disclose where the data is stored, and who can access it.

“And frankly, it shouldn’t be giving our data to anyone when its business is selling coffee and doughnuts!”

Source link

Jordon Hudson sues couple over shirtless Bill Belichick video leak

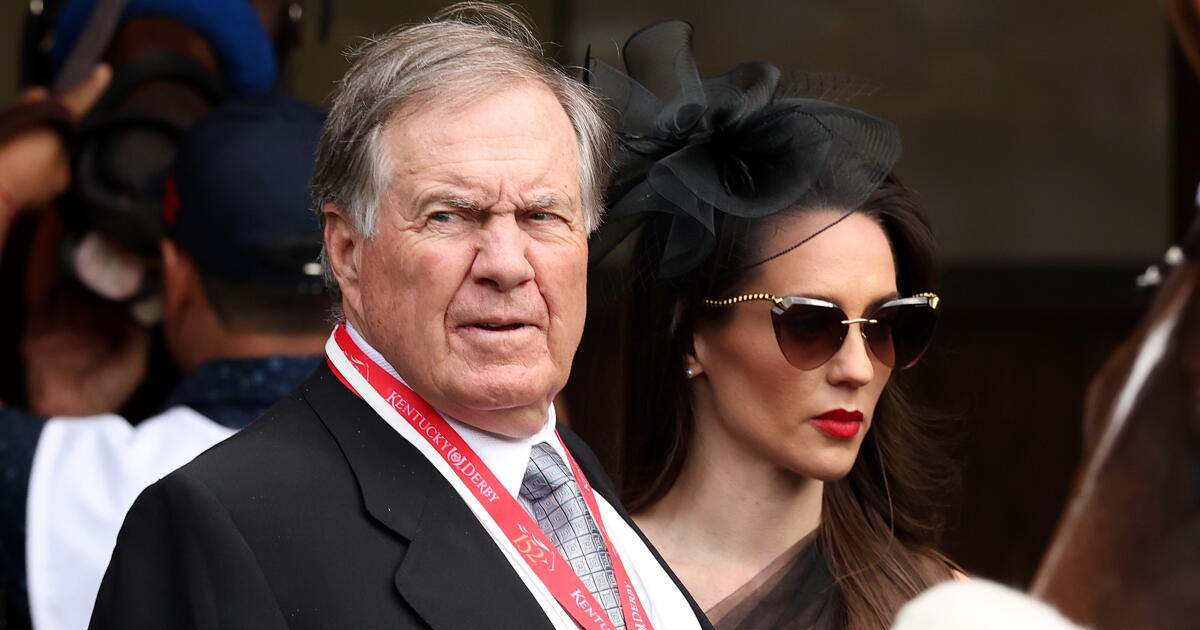
Jordon Hudson is suing the owners of a Massachusetts rental property for their alleged connection to the release of a video that showed her then-boyfriend Bill Belichick shirtless and outside the home while Hudson was renting it in 2023.

In a civil lawsuit filed Friday in Suffolk County Superior Court, Hudson accuses the couple of invasion of privacy, breach of contract and unfair and deceptive conduct after the video, which was captured on a porch security camera, and “personal and private information about Ms. Hudson” were leaked online.

According to the complaint, that leak in November 2023 was the reason the public found out about the romantic relationship between the then-22-year-old former college cheerleader and the then-70-year-old coach of the New England Patriots, who now coaches the North Carolina Tar Heels.

“These outrageous violations of Ms. Hudson’s privacy have, among other things, resulted in significant unwanted publicity and scrutiny of Ms. Hudson and her relationship with Mr. Belichick, which they had intended to remain private, and led to the ridicule and denigration of Ms. Hudson through numerous tabloid stories published by the media,” the complaint states.

“This unwanted scrutiny and the ensuing media stories, which contain false information, has caused significant damage to Ms. Hudson, which would not have occurred had Defendants not leaked Ms. Hudson’s personal and private information.”

The Times was unsuccessful in attempts to reach the defendants for comment.

The complaint states that Hudson booked the rental house for four days through Airbnb in or around June 2023. During her stay, the filing states, Hudson received a text from one of the owners reminding her not to park in front of a neighbor’s property. According to the complaint, the owner also texted Hudson “a link to a Ring video of a shirtless Mr. Belichick walking to and from the Property, which had been captured and saved without the knowledge or authorization of Mr. Belichick or Ms. Hudson (the ‘Ring Video’).”

Hudson then informed the defendant that privacy was important to them and asked if she could delete the video, the lawsuit states, to which she received the response: “We will delete it from ring, but as you know, unfortunately, videos are never totally deleted.”

After the video was leaked and the relationship became public, the complaint states, the same defendant told Hudson, “I absolutely did not leak this video to twitter or anyone.” But in May 2025, according to the filing, the owner told Hudson in a text that while they didn’t release the video publicly, “we had sent it to a few people initially wondering is this him [Mr. Belichick], isn’t it him and I don’t know what happened from there.”

The complaint also accuses the defendants of giving a second porch video of Belichick to journalist Pablo Torre, who aired it on his podcast that same month.

Hudson is requesting a jury trial and seeks unspecified damages and an order “enjoining Defendants from disclosing or disseminating any personal and/or private information related to Ms. Hudson to any third-party.”

Multiple media outlets reported last month that Hudson and Belichick quietly ended their romantic releationship in late 2025 but remain close friends and business partners.

Source link

The new ‘no frills’ business class seats with no TVs, privacy doors or reclining seats

BUSINESS class is a rare luxury – a chance for those with deep pockets to sip champagne, lie flat and catch the latest movies at 35,000 feet.

But what if the option to recline was taken away…

A new business class seat has no TV screen and doesn’t recline Source: SoFab – Optimares

As well as the large TV screen… Would you even be left with a business class seat? One airline thinks so.

Trinity Airways’ new business class seat features a sofa-like chair and a wraparound privacy screen… And that is it.

There is no recline option nor a TV screen.

The plane does have WiFi onboard so you can watch films on your own laptop or tablet though.

Read more on travel inspo

ALL IN

I found the best value all inclusive London hotel… just £55pp with free food & booze


SO FLY

Our fave beach hols under 5 hours from UK with Caribbean dupes & £2 bottles of wine

This ‘no frills’ seat is the new option on the South Korean budget carrier’s rebranded cabins on its new Airbus A330-900neo jets.

The seat is called SoFab and is despite being around since 2023, Trinity recently adopted the seat and is currently the only airline to have it onboard its planes.

Unlike most business class seats that recline, have a large – and usually – LED screen and a cosy lie-flat bed, SoFab instead takes it back to basics.

When you do want to sleep, you will have to pull a tab and a cushioned ottoman will slide out, filling the gap between the seat and the footwell to create the long bed.

This means you can sit upright with your legs stretched out or slouch down into the chair, lying across it and the ottoman.

Reports claim that SoFab’s bed is around 25 per cent larger than other business class seats.

Instead, there is a cushion ottoman as a foot rest Source: Trinity Airways
It means the seats are cheaper Source: SoFab – Optimares

In total it stretches, 198cm long (roomy enough for someone who is 6’5 to lie flat) and 102cm wide.

Across the cabin, these seats are arranged in a 1-2-1 layout so that each passenger can directly access the aisle.

Instead of each seat featuring a door, a curved shell wraps around the passenger acting as a privacy screen,

And for the two passengers in the middle of the plane, there is also a privacy divider between them.

Of course, like most seats, there is air conditioning as well as a USB socket.

As for when it comes to meal time, the tray table can also be a side table – which means passengers don’t have to fully collapse the table just to get up and pop to the loo.

And because the seats down have a screen, the plane is cheaper to fly, which also means cheaper tickets.

While Trinity Airways doesn’t fly direct from the UK, a one-way trip from Rome to Seoul for example, costs around £1,296.21 for a business class seat in December.

In comparison, a one-way trip from Rome to Seoul with Korean Air in business class costs around £1,816.96.

Source link

Trump administration attempts to take down leak of ICE personnel data | Donald Trump News

An Icelandic web company, FlokiNET, has defended the data’s publication as satisfying a ‘legitimate’ public interest.

The United States Department of Homeland Security (DHS) has asked an Icelandic web hosting company to take down a site with information about tens of thousands of its employees.

On Thursday, the Icelandic company FlokiNET posted a letter it received from the cybersecurity firm ZeroFox, on behalf of DHS.

Recommended Stories

list of 3 itemsend of list

The letter accused FlokiNET of violating its terms of service by publishing a “stolen” employee dataset and asked it to “remove or disable” the information.

“The content is live and places more than 40,000 identifiable individuals at risk of harassment, stalking, and physical harm,” the letter said.

FlokiNET said the letter concerned one domain, icepi.cx, which has compiled information about employees from a range of DHS agencies, including Immigration and Customs Enforcement (ICE) and Customs and Border Protection (CBP).

Those agencies have come under intense scrutiny since the start of President Donald Trump’s mass deportation campaign in 2025.

But the Trump administration has often refused to identify DHS agents involved in specific operations, citing safety risks.

Though FlokiNET said it refused to comply with DHS’s request, it noted that the website’s registrar ultimately suspended the domain. The employee information has since moved to a different domain.

In a statement posted online, FlokiNET defended its decision not to remove the site.

“Federal officers carrying out an enforcement programme are not private individuals while they are carrying it out,” the company said. “The public has a legitimate interest in knowing who is doing that work, under whose authority, and in which office.”

The database was first posted online on Wednesday by Distributed Denial of Secrets (DDoSecrets), a group that showcases leaked government data.

In the past, DDoSecrets has released emails from convicted sex offender Jeffrey Epstein, as well as information from the Israeli Ministry of Justice and police departments in the US.

A hacker group calling itself the “Department of Peace” has claimed responsibility for obtaining and sharing the DHS data.

Since the database was first published, other groups have spread the information elsewhere, including on sites like icepi.cx. As a result, the information is unlikely to be entirely scrubbed from the internet.

The Trump administration, however, has taken an aggressive approach to online platforms purporting to contain information about ICE employees and other agents involved in immigration operations.

Last year, for instance, the US Department of Justice pressured tech giants like Apple to remove apps that track ICE agents, including one called ICEBlock.

The move sparked backlash from Democrats and free-speech advocates, who argued that the public has a right to report on ICE’s movements.

“Blocking access to these apps at the request of the federal government raises the distinct possibility that Apple is working with government to violate its customers’ First Amendment right to record and report on the activities of their government,” Democratic Representative Jamie Raskin wrote in a letter last year, asking Apple to review its decision.

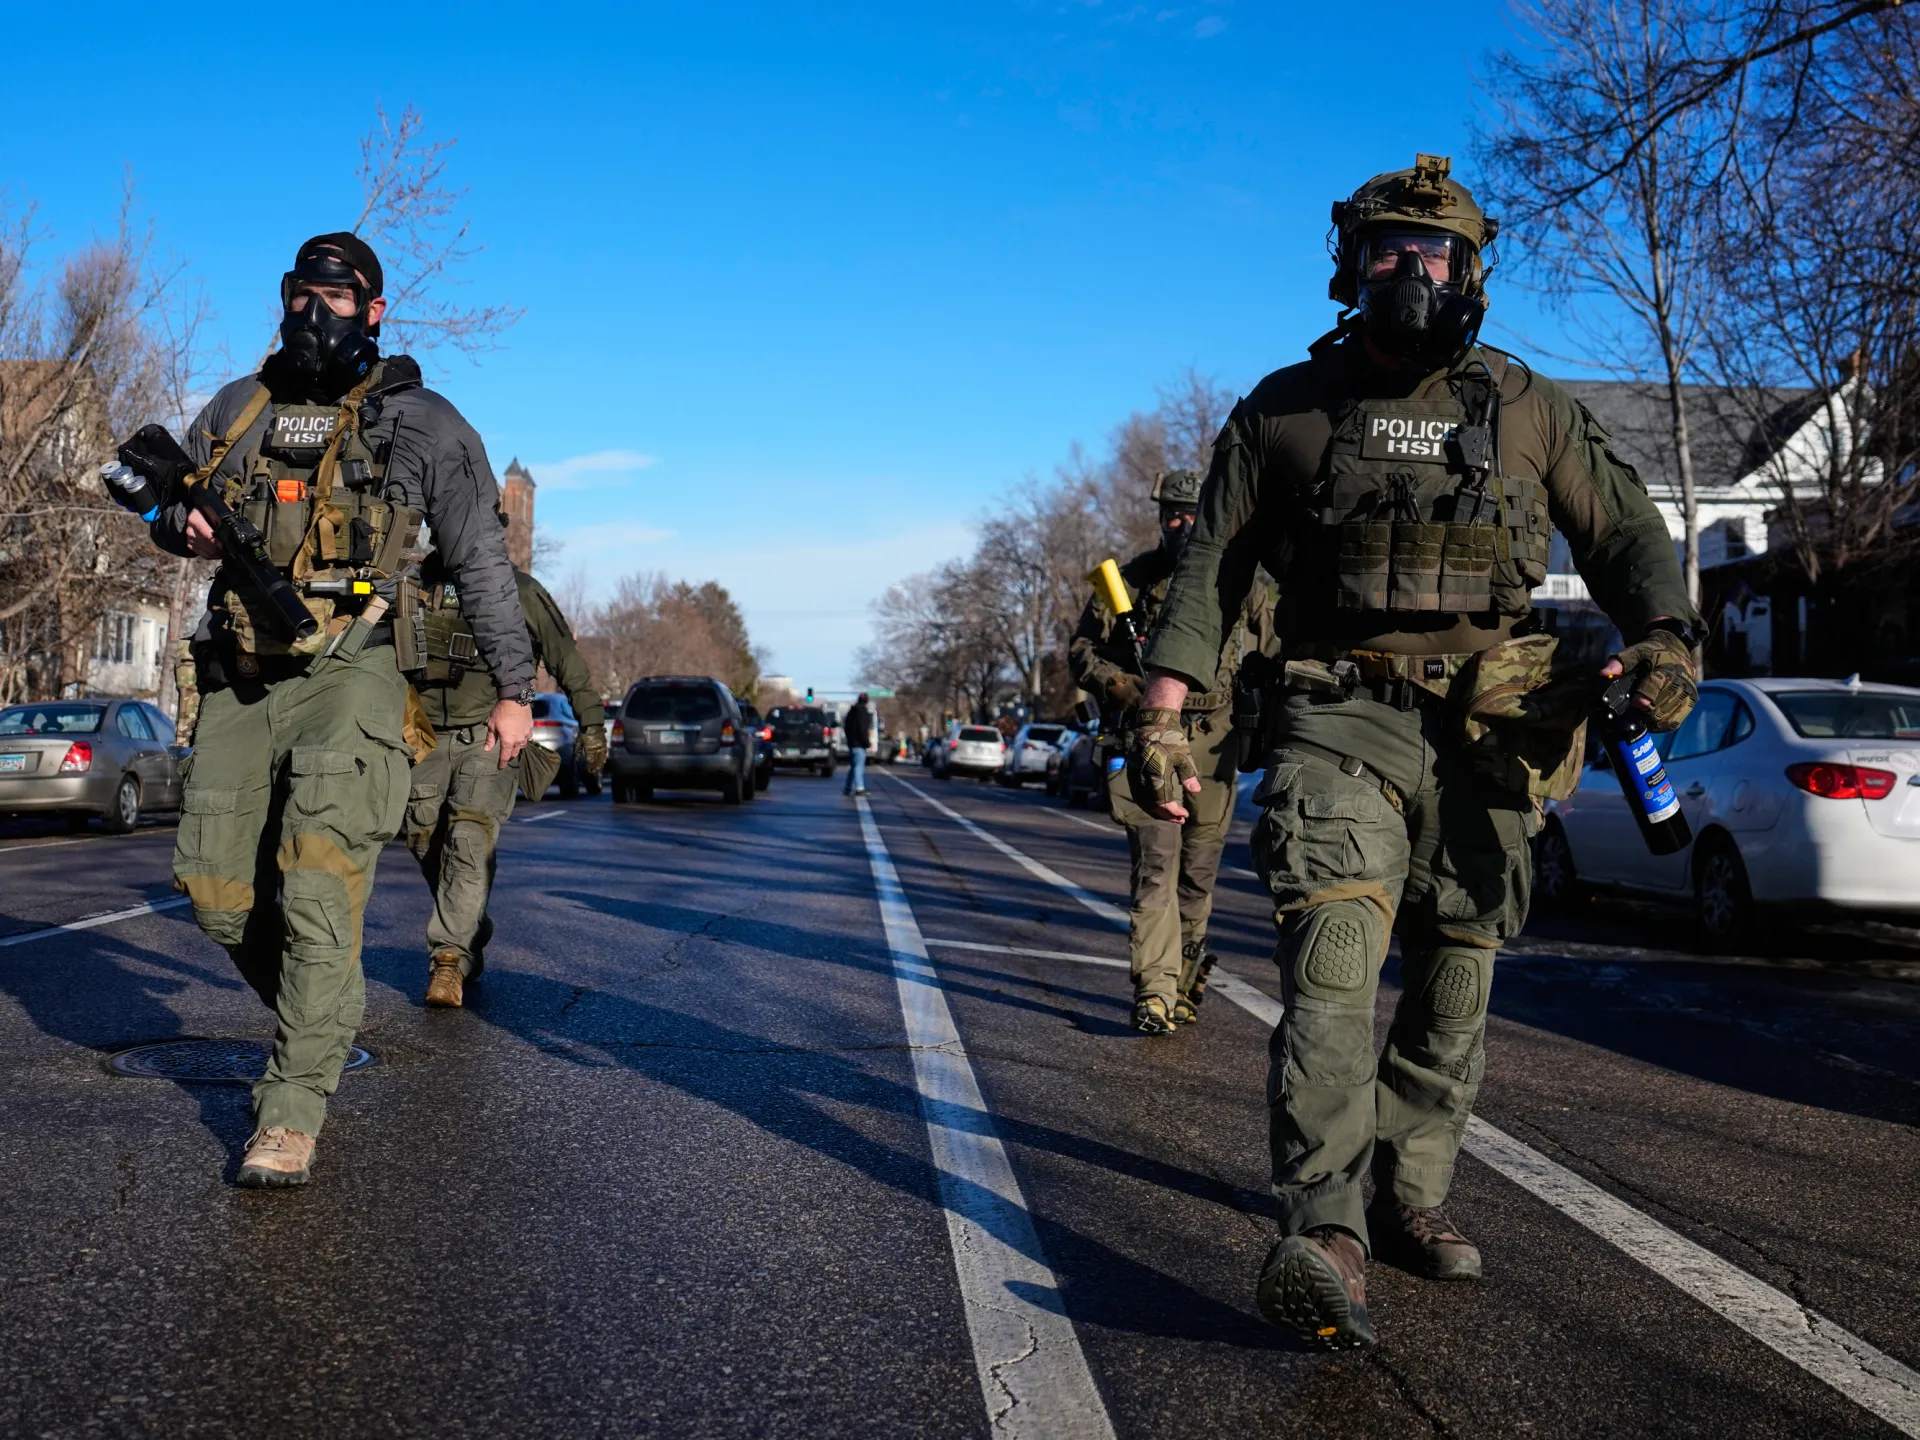
Immigration agents, meanwhile, have taken several steps to conceal their identities during operations, including wearing face masks or street clothes.

That lack of transparency has spurred criticism from human rights groups and immigration advocates, who argue that they have little recourse to pursue allegations of excessive force or impropriety during ICE raids.

Since Trump was sworn in for a second term, at least 25 people have faced gunfire from immigration agents. Six of the shootings have resulted in deaths.

Other cases have involved alleged violations of civil liberties – including unlawful arrests and racial profiling – as well as controversial tactics like car ramming and tackling.

Source link