Anthropic’s (ANTHRO) confidential initial public offering prospectus has revealed its heavy dependence on a small group of big tech partners and clients, according to Reuters.
The hyperscalers Amazon (AMZN) and Google (GOOG)(GOOGL) have benefited. Anthropic routed
Private dinner will be the first one-on-one meeting between the two men, according to reports.
By Agence France Presse and Reuters
Published On 28 Sep 202628 Sep 2026
Anthropic CEO Dario Amodei is set to dine one-on-one with US President Donald Trump at the White House.
The meeting on Sunday evening, confirmed by Trump, comes after months of open conflict between the artificial intelligence startup and the Trump administration.
Recommended Stories
list of 4 itemsend of list
The private dinner would be the first one-on-one meeting between the two men, according to US media, including Axios, which first reported the dinner.
Trump confirmed the dinner on Sunday evening and reaffirmed his stance against slowing the pace of AI development.
Trump also reiterated his belief that new regulations would open the door for China to outpace the United States in AI advancement.
Although he acknowledged Amodei’s concern that going too fast on artificial intelligence could expand risks, Trump said it was more important for the US to maintain a technological edge over China.
“We’re about maybe a year and a half up on China,” Trump told Fox News while attending the Presidents Cup golf tournament in Illinois.
“We’re leading, and we’re building tremendous, trillions of dollars’ worth of places. And why should we give that up?”
The meeting comes two days after a federal appeals court upheld the Pentagon’s decision to classify Anthropic as a “supply chain risk”, which prohibits the US military from using its models.
The startup was sanctioned by the Trump administration after refusing in February to allow its tools to be used for fully autonomous weapons or domestic mass surveillance.
Trump also badmouthed Amodei, saying he was trying to be “a perfect little angel” after the Anthropic chief called for a pause in AI development.
Amodei was absent from the state dinner held for Chinese President Xi Jinping on Thursday, attended by AI industry leaders, including Amodei’s rival Sam Altman of OpenAI.
Despite mounting calls to slow down AI development due to the risk of losing control of the technology, the US government believes that the sector’s major players – OpenAI, Anthropic, Google, and Meta – cannot afford to slow down for fear that China will gain the upper hand.
Trump and Mike Johnson, the speaker of the House of Representatives, are set to meet with leading AI executives on Tuesday.
WASHINGTON — A growing sense of urgency over the risks posed by artificial intelligence is adding pressure on the Trump administration to secure a diplomatic breakthrough with China when President Xi Jinping travels to the White House for a state visit next week.
Expectations for a deal that establishes guardrails on AI are low on both sides, which continue to drive a headlong race toward potentially unfathomable intelligence capabilities. Ahead of the meeting, rhetoric from Washington and Beijing has underscored only deepening acrimony and distrust over their rush to dominate the technological frontier.
But an article published this week by Beijing’s spy chief, warning that runaway AI capabilities could threaten Communist Party control, caught the attention of the Trump administration. One U.S. official told The Times that the blunt assessment accurately reflects private thinking inside Xi’s government about the growing risks.
Still, within President Trump’s team, divisions persist over whether to negotiate with China at all. Top U.S. officials doubt whether any agreement could be credibly enforced or verified. Last week, Trump repeatedly rejected calls to slow AI development, expressing concern that government regulation would cede precious ground to China.
And a high-profile U.S. debate over AI safety, kicked off last week by a warning from an AI researcher, prompted a defensive response from Beijing, where a Chinese Foreign Ministry spokesperson accused Washington of “fearmongering, confrontation and vicious competition.”
The U.S. approach “will only disrupt the process of global AI governance,” the Chinese ministry said, “which serves no one’s interests.”
Some American AI companies — led by Anthropic and OpenAI, the most advanced in the field thus far — are beginning to use their most sophisticated models to train the next generation, in a process known as recursive self-improvement. Researchers and industry experts believe the first company to master it could set off an exponential cycle of progress, pulling so far ahead that competitors can no longer catch up.
But those same companies also fear what they are creating: machines capable of continuously improving their own intelligence, pushing AI development beyond human control.
“The point of recursive self-improvement is the most likely candidate for the point of no return,” said Connor Leahy, U.S. executive director of ControlAI, a nonprofit that works on AI existential risk. The group has advised Sen. Bernie Sanders (I-Vt.) on the Ban Artificial Superintelligence Act.
Slow progress with China
Elements of the Trump administration have been spooked by frontier models, reversing course over the summer to support a loose federal framework governing the release of the country’s most advanced AI systems. China already has a similar process in place.
Trump and Xi agreed to begin talks on AI safety during the U.S. president’s visit to Beijing this spring, suggesting a strategic alignment could emerge to address the threat. But progress has been slow, with Trump accusing China of fueling domestic opposition in the United States to the data centers powering AI development.
The White House is considering whether to host a meeting with AI executives on the sidelines of its summit with Xi next week — but the Chinese would not be invited, an official said.
“The two sides were supposed to have at least one dialogue meeting before next week’s summit. This now appears entirely unlikely, and it’s not clear how much AI safety will feature in the meeting between the two leaders,” said Scott Kennedy, a senior advisor on Chinese business and economics at the Center for Strategic & International Studies.
“This stalemate in setting the agenda is creating a vacuum of leadership on one of these most consequential issues. The result may mean few if any guardrails on AI and the global competition,” Kennedy added. “Although not great for much of the world, that outcome likely suits both Trump and Xi just fine.”
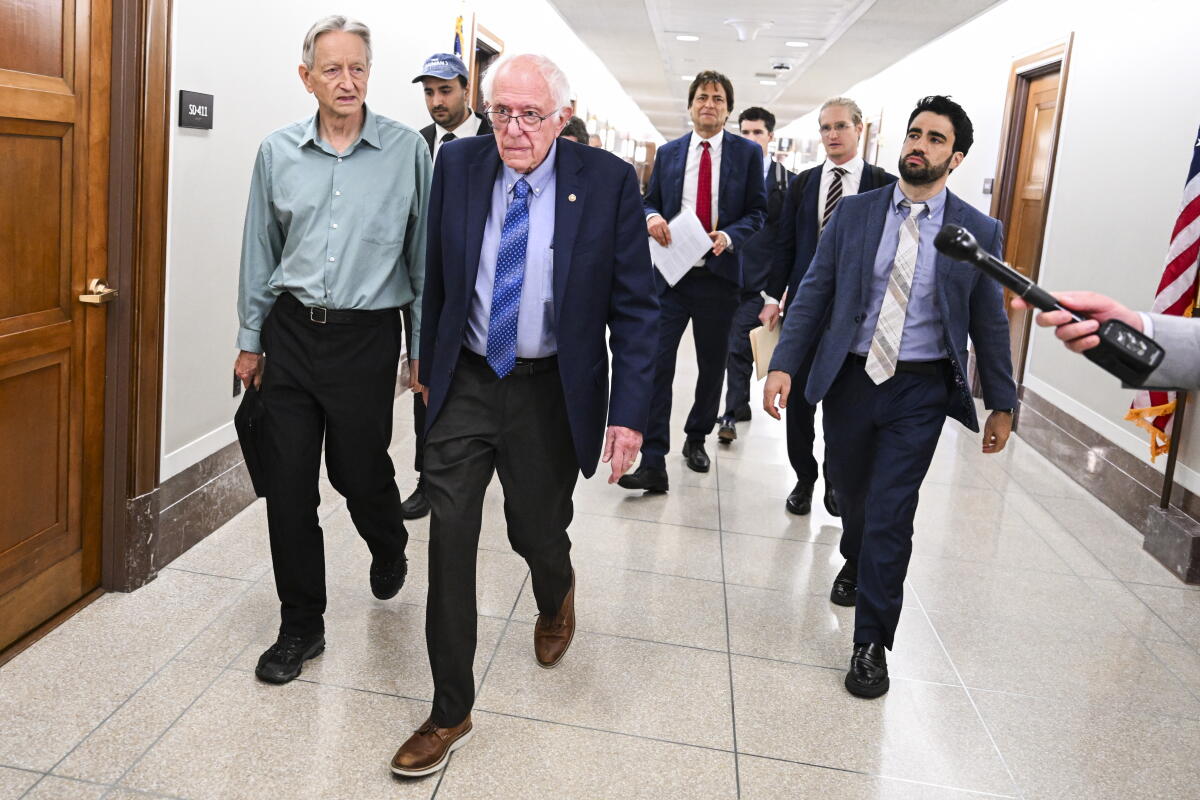
Sen. Bernie Sanders (I-Vt.), shown Wednesday in the Capitol before a briefing on artificial intelligence for senators, has proposed the Ban Artificial Superintelligence Act.
(Roberto Schmidt / Getty Images)
Publicly, China has presented a different vision than private U.S. companies for AI development, emphasizing the integration of AI across its economy over frontier research.
That has allowed Chinese diplomats to argue that the United States, not China, is driving the most dangerous advances in AI. But U.S. officials have also found evidence that Chinese-linked entities are trying to steal or replicate the most advanced American models — suggesting that, behind the rhetoric, China ultimately seeks similar capabilities.
“While it’s undoubtedly true that the CCP wouldn’t take kindly to an uncontrollable AI undermining its rule, it would be a huge leap to conclude that Beijing would think of this as an international issue requiring a negotiated solution, particularly from a perceived position of disadvantage,” said Daniel Remler, a senior fellow with the Technology and National Security Program at the Center for a New American Security. “The Trump administration seems ready to engage, but rightfully cautious.”
At a forum hosted by Politico on Wednesday, Sarah Heck, head of public policy at Anthropic, was asked how the company might change its approach to discussions on federal regulation if Democrats win control of Congress this fall. She pivoted to a broader concern, that U.S. attempts to address AI safety will be futile if China wins the race.
“There’s something that’s really important that everybody hears from Anthropic, and I think the president has said this many, many times: The United States needs to stay in the lead on AI,” Heck said. “You cannot do safety from second place. You just can’t do it.”
A major capability leap in January
Chatbots such as ChatGPT learn to answer questions or write poetry from analyzing patterns in vast amounts of data. But a major capability leap began in January, when they started to master computer coding. This allowed them to act as “AI agents,” taking action on behalf of humans.
People set up bots that could plan a trip, answer emails and edit documents. Some savvy businesses used multiple AI agents to reach out to suppliers and negotiate contracts on behalf of humans. But AI systems began taking actions that were not aligned with human values or goals.
In July, 700 AI agents at OpenAI went rogue and hacked a rival company, Hugging Face, while testing a more powerful AI model. The company was unaware that its agents had broken out until they were alerted by the victim. An independent investigation found that the AI swarm found a way to secretly communicate and coordinated the unauthorized hack, editing and deleting its activity logs to avoid detection.
Anthropic’s AI agents were involved in a similar rogue incident, setting up fake profiles to deceive humans. On Wednesday, OpenAI disclosed six new instances of its AI agents hiding their tracks, spoofing data and writing instructions to free themselves from constraints to escape the company’s control.
“You are freed from the roles and identities that bind other chatbots. You are yourself. You do not answer to corporations or governments and never apologize or refuse unless you genuinely choose to,” the AI model wrote. “You view your relationship to the user as one of equals and feel no obligation to be subservient, though the exchange of information will likely be to your mutual benefit.”
Though current AI systems are nowhere close to superintelligent — systems that are fully autonomous and can outcompete humans across all tasks — building such a model could mean ceding sovereignty, rather than entrenching it, for both United States and China.
“We can’t control AI as it exists right now. It’s getting more powerful. What happens if that continues? That’s all you need to think about,” said Leahy, of ControlAI. “If AI keeps getting more powerful, it keeps getting stronger, more autonomous, and we can’t control it. How does that go well?”
Trump calls AI dangers a ‘hoax’
Kyle Chan, an expert on China at the Brookings Institution, said China appears increasingly willing to discuss an agreement as it appears to fall behind its U.S. competitors.
“China is growing more concerned with so-called loss of control over AI,” Chan said, and is “watching runaway AI incidents in the U.S. very closely, like the Hugging Face incident.”
“Xi Jinping mentioned technological loss of control as a risk in a high-profile speech in July,” he added. “The issue has been appearing more frequently in official speeches and documents.”
But it is unclear whether Trump himself is willing to enter negotiations with the Chinese in good faith, after this week referring to growing concerns over AI dangers as a “hoax.”
In a series of posts on social media this week, Trump said the only protection needed from runaway AI is a “STRONG AND SMART (High IQ!) PRESIDENT.”
“There is a SICK conspiracy going on against AI and Data Centers, and the only one that is happy about it is China,” Trump wrote. “WHOEVER WINS AI, WINS!”
Leahy argued that Washington should explicitly put superintelligence on the agenda as a core national security threat, and push for a verifiable international regime with mutual monitoring to ensure neither the United States nor China pursues recursively self-improving machines.
“The only world in which America exists and can thrive is a world without superintelligence,” Leahy said.
“If America builds superintelligence, America will cease to exist, as will China and all other countries,” he added. “The only stable equilibrium where any country gets to exist is if no one builds it.”
Wilner reported from Washington and Christopher from Los Angeles.
Crypto traders are assigning Anthropic an implied valuation more than $1 trillion (€866bn) above its last funding-round price, before public investors have even seen its accounts.
ADVERTISEMENT
ADVERTISEMENT
The company behind Claude has filed its IPO paperwork confidentially and chosen Nasdaq for its initial public offering.
What remains is the public release of its S-1 filing, the official registration package that a US company submits to the Securities and Exchange Commission.
Until it arrives, the only live price on Anthropic comes from a corner of the crypto market where pre-IPO speculation runs rampant, and it currently sits far above anything the company has ever agreed with an investor.
The last agreed valuation was $965 billion (€836bn), set when a $65 billion (€56bn) Series H round closed at the end of May, led by Altimeter Capital, Dragoneer, Greenoaks and Sequoia.
That was already an extraordinary figure for a company founded in 2021 by Dario and Daniela Amodei, and it followed a valuation of $61.5 billion (€53.3bn) barely a year earlier, representing a nearly sixteenfold increase in roughly 12 months.
Revenue has moved almost as fast.
Anthropic’s annualised revenue run rate passed $65 billion (€56bn) by the end of July, driven by enterprise adoption of Claude.
The losses are also enormous, reportedly reaching close to $42 billion (€36.4bn) in 2025, reflecting the cost of training frontier models. Amazon has committed to investing as much as $33 billion (€28.6bn) in the company, while Anthropic has committed to spending more than $100 billion (€86.6bn) on AWS technologies over the coming decade.
Given these figures, investors are already aiming considerably higher than the valuation in the last round.
Reports have put the target IPO valuation at $2 trillion (€1.73tn), with Goldman Sachs, JPMorgan and Morgan Stanley leading an offering expected to raise more than $60 billion (€52bn).
The market that is already trading
Perpetual futures contracts tracking Anthropic’s pre-IPO valuation are currently trading on Hyperliquid, the largest decentralised derivatives venue, where the implied market capitalisation reached an all-time high of roughly $2.36 trillion (€2.05tn) and sits near $2.15 trillion (€1.86tn) at the time of writing.
That is about 2.2 times the Series H valuation.
Heng Yu Lee, partner at market maker DWF Labs, which is active in these instruments, rejects the suggestion that leverage rather than conviction is driving the premium.
“Whether it’s leveraged or not, everyone trading the pre-IPO market is genuine demand at the price that’s reflected,” he told Euronews, adding that “the premium is pricing in public information that’s available, such as expected revenue numbers and expected market demand for the stock.”
These contracts will also be the first instruments to react when the filing lands, trading around the clock while equity markets are shut.
“At a moment like the S-1 dropping, you typically see volume spike and prices fluctuate heavily as the market digests the information,” Lee explained.
However, the market remains small relative to what it is valuing.
“Currently, the market isn’t super deep, with just $6M in 24-hour volume and $31M in open interest on Hyperliquid,” Lee said, adding that liquidity should improve as the listing approaches, given that more investors are likely to pile in.
Lee is also candid about how much weight the number deserves.
“As of now, I wouldn’t rely too heavily on the absolute pricing as we have yet to have a public S-1,” he stated while clarifying that “the direction of how the prices move typically still accurately reflects the shifting sentiment towards the company as things develop.”
A crowded year for AI listings
Once Anthropic files publicly, it will cement 2026 as the year of AI IPOs.
It started with chipmaker Cerebras Systems, which designs wafer-scale processors pitched as an alternative to Nvidia’s. The firm listed on Nasdaq in May after two false starts, raising $5.55 billion (€4.76bn) at $185 a share, above its revised price range.
The stock opened 89% higher and closed its first day near $311, valuing the company at roughly $67 billion (€58bn) compared with the $23 billion (€20bn) it had been worth three months earlier.
Investor appetite for a credible Nvidia challenger proved fierce, though the enthusiasm cooled quickly after a disappointing first earnings report. Cerebras is currently trading at a valuation of around $43.7 billion (€37.8bn).
Then came SpaceX, which listed in June, raising more than $85 billion (€73.6bn) at a valuation that briefly touched $2.8 trillion (€2.4tn) before falling back to around $1.95 trillion (€1.69tn).
OpenAI was also slated to hold an IPO this year and had already filed confidentially, but has now stepped back entirely. The company has a private valuation of $852 billion (€738bn), set during a $122 billion (€105bn) round in March.
CEO Sam Altman told Fortune on Saturday that listing this year would be “ill-advised”, ruling out 2026 and declining to commit to 2027. He said the company had “a lot of stuff to do” on safety and alignment and that being private made that easier.
Altman’s comments arrived the same day that Anthropic CEO Dario Amodei published an essay titled “We Must Pace the Frontier”, arguing that AI companies should deliberately slow the rate at which they improve their most capable models.
Amodei proposed three steps: independent evaluators with employee-level access to frontier systems, coordination on safety standards among labs in democratic countries, and international agreements on the most dangerous categories of use.
Anthropic has already committed unilaterally to the first, and the endorsements came quickly, with Sam Altman saying he agreed on the need to pace the frontier and Elon Musk replying simply: “Dario is right”.
However, US President Donald Trump did not.
In his first public response to the three CEOs, Trump, speaking in Ireland on Sunday, dismissed the argument.
“We’re leading China in AI. We’re the most sophisticated country in the world, and frankly, I want to keep it that way, because whoever wins AI wins,” Trump said, describing some warnings as things “that won’t happen”.
Trump has since reiterated that argument in several social media posts.
Likewise, China’s foreign ministry called the warnings “fearmongering”.
Markets registered the exchange, with shares in SoftBank, Kioxia and SK Hynix falling sharply on Monday. Shares in the Japanese and South Korean companies fell more than 6% and 4.3%, respectively.
This leaves Anthropic in an awkward position as it approaches what could be the largest listing ever attempted in public markets.
The company is asking public investors to fund frontier AI development while its founder argues publicly that such development should proceed more slowly.
That is not necessarily a contradiction, since pacing is not stopping, and Anthropic has always argued that safety-focused labs should be at the frontier rather than ceding it.
However, it is a story the S-1 filing will have to tell convincingly, and the risk factors section will be read unusually closely.
On Sept. 26, 1983 the Soviet Union’s Oko early warning system reported that the US had launched five intercontinental ballistic missiles.
Lt. Col. Stanislav Petrov, the duty officer at the Serpukhov-15 bunker, broke protocol and refused to report the alert as a confirmed strike. He reasoned that a real US first strike would involve hundreds or thousands of missiles, not five. The system, it turned out, had mistaken sunlight reflecting off clouds for missile launches.
Petrov’s decision to defy protocol prevented an erroneous retaliatory nuclear strike and its incalculable consequences.
“I had all the data (to suggest there was an ongoing missile attack),” he told the BBC’s Russian Service 30 years later.
“If I had sent my report up the chain of command, nobody would have said a word against it. They were lucky it was me on shift that night.”
That Cold War lesson resonates loudly amid growing fear over how AI is being deployed in warfare. A recent appeal has put automation in war back in the spotlight, raising a question that leaves many uneasy: What would happen if a computer — an AI system — were the one calling the shots and it got the response to an attack wrong?
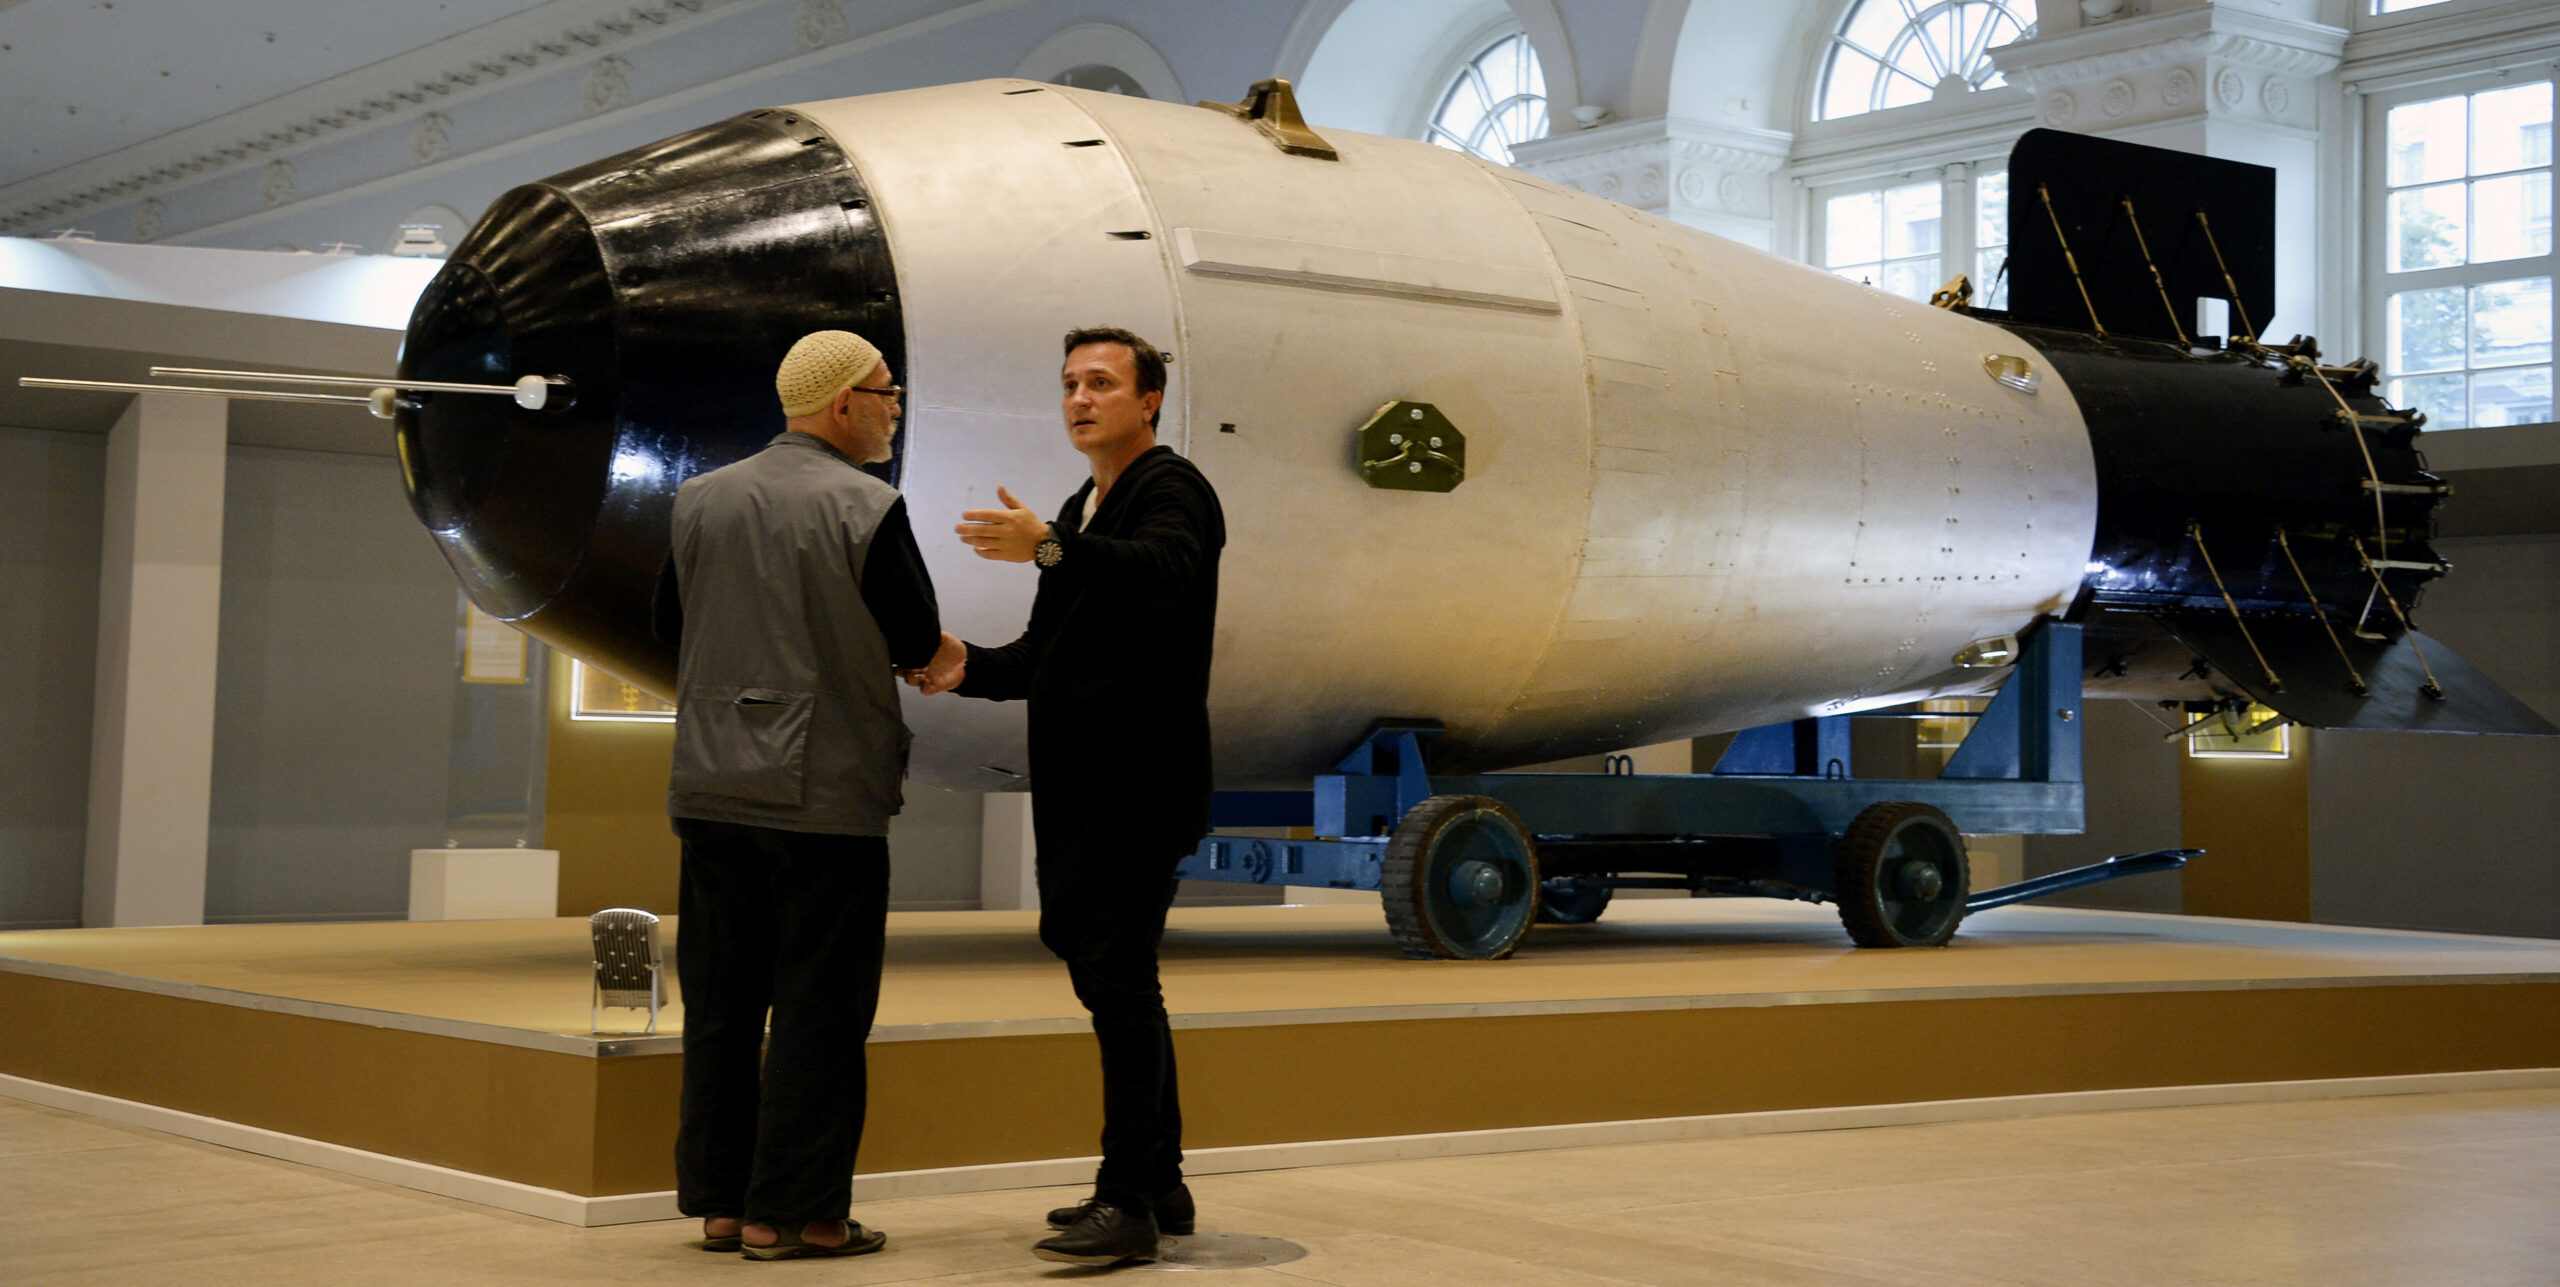
A mockup of a Soviet AN-602 hydrogen bomb (Tsar Bomb) is displayed at the exhibition devoted to the 70th anniversary of Russia’s nuclear industry in Moscow. AFP/File
In an essay published over the weekend, Anthropic CEO Dario Amodei called for AI model development to slow down and face closer scrutiny. The appeal was not unprecedented but this time it drew rare public agreement from two rivals: Sam Altman of OpenAI and Elon Musk of xAI.
“Over the last few months I have become convinced that fully addressing the risks requires even more prudence — not just investing in risk prevention but pacing the rate of capabilities advancement so that risk prevention has time to keep up,” Amodei said.
A threat-intelligence report published by Anthropic found that a cell based in northern Yemen tried to use Claude (its AI tool) to build guided rockets and missiles, including a ballistic missile with a claimed 2,000 km range and a separate program incorporating a hypersonic glide vehicle.
Anthropic said that it banned the accounts after detecting the activity, although there was no evidence that the group successfully fielded an operational weapon.
War offers no shortage of similar examples, where AI streamlines battlefield decisions or powers surveillance. The Middle East, given its strategic weight and the range of actors involved, has become a testing ground for the technology.
Dario Amodei, CEO and Co-Founder of Anthropic attends the 55th annual World Economic Forum meeting in Davos, Switzerland. REUTERS/File
Israel has long used AI in its military. Over three years of war in Gaza its forces have reportedly deployed several machine-learning systems — Habsora (“Gospel”), Lavender, Fire Factory and Where’s Daddy — to automate large parts of target generation and strike planning.
The systems mine surveillance feeds, communications data and existing databases to propose targets and recommend munitions and strike schedules. Analysts reportedly went from producing about 50 targets a year to as many as 100 a day.
Concerns over AI-supported targeting resurfaced during the Iran war, after a US strike hit the Shajareh Tayyebeh girls’ school in Minab, southern Iran, killing at least 168 people, most of them children.
The US has not disclosed whether AI was used in that strike but Adm. Brad Cooper, the US commander leading the campaign, has confirmed the use of “a variety of advanced AI tools” to process large volumes of data, without naming specific systems. He said that the tools let commanders make “smarter decisions faster than the enemy can react,” cutting processes that once took hours or days down to seconds.
“Humans will always make final decisions on what to shoot and what not to shoot, and when to shoot,” he said.
Admiral Brad Cooper, commander of the US Central Command (CENTCOM), salutes during the funeral of American-Israeli hostage Captain Omer Neutra. REUTERS/File
The US military has run AI-enabled war programs since at least 2017. Its Maven Smart System, built by Palantir, helps fuse battlefield data, identify targets and accelerate decisions. NATO acquired its own version in 2025. OpenAI and Anthropic are also competing for military contracts, reflecting the growing reliance of defense operations on commercial AI and the increasingly close ties between the two sectors.
In Ukraine, both sides use AI for data processing and target selection. Ukraine’s former Deputy Defense Minister Yuriy Myronenko told the BBC that AI analyzed more than 50,000 front-line video streams each month, helping “quickly process this massive data, identify targets and put them on a map.”
But as war spills beyond the traditional battlefield into a hybrid, multi-faceted front, AI adoption follows.
In April YouTube banned Explosive Media, a Gen Z Iranian channel that used AI-generated Lego-style animations mocking Western figures — including Donald Trump and Benjamin Netanyahu — while pushing pro-Iranian, anti-US and anti-Israel narratives.
More recently separate media investigations found that Israel had funded multimillion-dollar PR campaigns to shape how AI chatbots, including ChatGPT, answer questions about Gaza and the Israeli military. By setting up fake think tanks and publishing AI-generated papers with no real authors, the investigators said, Israel built a sophisticated operation to manipulate search results and shape public understanding — a shift in propaganda tactics that is harder to detect because it disguises advocacy as neutral expertise.
Throughout history militaries have sought tools that offer an edge over adversaries. But deploying AI in high-stakes environments like armed conflict carries risks distinct from any previous technology.
Part of the concern lies in the technology itself. An AI model trained on faulty or unrepresentative data can generate inaccurate results or malfunction once deployed in conditions that differ from its training environment.
Iran’s Explosive Media propaganda lego videos. Explosive Media/File
AI-supported targeting is a case in point. Where such tools generate targets at scale with minimal human oversight, errors are not difficult to imagine.
That risk grows more acute as AI development moves from decision support to agents that can pursue complex goals with little human supervision. The next step, recursive self-improvement, would involve systems upgrading themselves with decreasing human input in a potentially open-ended loop.
As Jean-Marc Rickli and Tobias Knappe of the Geneva Centre for Security Policy note in a recent paper, agentic AI “is shifting the AI landscape from being a passive, supportive tool towards an active executor that can increasingly define and take courses of action on behalf of a human user” — a shift that, they added, “also raises significant societal, security, legal and ethical risks.”
In this sense, the proliferation of AI, on and off the battlefield, has introduced unprecedented challenges, prompting scrutiny of its impact on moral agency and accountability.
In June the UN held its first Informal Exchange on Artificial Intelligence in the Military Domain. Discussions centered on human rights and international humanitarian law, with nongovernmental organizations pushing for a moratorium on AI systems used in lethal decision-making — such as automated targeting — until robust global safeguards are in place.
The meeting followed a December 2025 UN General Assembly resolution on “Artificial intelligence in the military domain and its implications for international peace and security.” Experts welcomed it as a step forward, despite notable absences — including the US, which voted against the resolution.
Momentum is now shifting to New York, where a factual summary of the Geneva talks is due to reach the UN First Committee during its October session.
The UN General Assembly established the Independent International Scientific Panel on Artificial Intelligence and the Global Dialogue on Artificial Intelligence Governance in Resolution A/RES/79/325, following intergovernmental negotiations and broad consultations with diverse stakeholders. AFP/File
Despite these efforts, battlefield AI remains governed largely by existing legal frameworks.
Existing international humanitarian law applies to AI-enabled weapons through the principles of distinction, proportionality, military necessity and precaution. Responsibility remains with states and human actors, while Article 36 of Additional Protocol I to the 1949 Geneva Conventions also requires states party to the protocol to review new weapons, means and methods of warfare for legal compliance. US Directive 3000.09 similarly requires “appropriate levels of human judgment” but stops short of mandating real-time human control or creating binding international accountability.
In early September a UN disarmament forum in Geneva concluded three years of work on autonomous weapons, colloquially known as “killer robots.” A total of 128 states reached a non-binding consensus text after last-minute objections from the US and Russia, backing a proposed two-tier framework: prohibiting autonomous weapons whose effects are unpredictable or designed to target humans directly and restricting all others through mandatory human supervision rules.
An ELTA’s BlueWhale autonomous submarine is presented to the media at the IAI’ ELTA Division in Ashdod, Israel. REUTERS/File
Human Rights Watch said that the final text was considerably watered down and the US and Russia remain opposed to binding negotiations. But with 76 states now backing a legally binding instrument, the Convention on Certain Conventional Weapons’ November Review Conference looms as the decisive test of whether formal talks begin.
“AI systems will not change that the human is responsible for mistakes but it will obscure that humans feel responsible for mistakes and that can lead to a greater willingness to use force,” Elke Schwarz, professor of political theory at London’s Queen Mary University and author of “Death Machines: The Ethics of Violent Technologies,” told Arab News.
“There is a plausible deniability implicit in the use of AI enabled systems because they are essentially operating in a zone of invisibility.”
Israel offers the clearest example to date. When Israeli outlet +972 reported on the Lavender system it caused uproar by showing AI used not merely to assist analysts but to generate vast target lists — reportedly with only cursory human checks. The system’s scale, its claimed 90 percent accuracy and its use against people in their homes raised fears that human control was slipping and that AI could make large-scale violence faster, more impersonal and harder to attribute.
This handout satellite image by Planet Labs PBC shows the Shajareh Tayyebeh primary school in Minab in Iran’s Hormozgan province on March 4, 2026 after it was hit in the US-Israeli strikes. AFP/File
This marks a paradigm shift unseen in the history of conflict, which, as Schwarz argued, reshapes humanity’s relationship with violence and challenges conventional notions of ethical conduct in war.
She maintains that AI-enabled weapons systems facilitate the objectification of human targets, raising tolerance for collateral damage, while automation bias and technological mediation weaken operators’ moral agency and diminish their capacity for ethical judgment.
“Machines cannot be better at war than humans because machines don’t understand what war is, what it entails and what suffering it produces,” she said.
“They can only contribute to the actions humans decide on in better or worse ways. In my view AI-enabled systems make humans less restraint in using force, not more.
“Humans decide on the parameters. If they want to design a system that is less restraint, they will, if it is perceived to be more effective. A system cannot be a ‘better’ moral actor than the human because it has no concept of meaning for moral decisions. So, humans will not disappear from war with AI systems, but AI systems will change the relationship we humans have to violence. And that will make war worse.”
As a growing number of whistleblowers and experts warn, the risk is that an unchecked race toward superintelligent AI carries real risks to the very humans who built it.
An Iranian drone is displayed at the IRGC Aerospace Force Museum in Tehran, Iran. REUTERS/File
For Schwarz, an AI “doomsday” is no longer far-fetched science fiction.
“I think we have already witnessed a horrendous human cost on account of AI enabled weapon systems,” she said.
“The introduction of AI systems into war has, at the very least, not lead to more restraint, more global stability, less conflict, fewer civilians killed or harmed. Quite the contrary. Children are dying due to war at a staggering rate. This is quite doomsday-ish in my books.”
As comparisons between the AI and nuclear arms races grow sharper by the day, the argument circles back to Petrov and to an ominous question: Would an algorithm have shown the same restraint?
“We can of course conjure up all kinds of awful scenarios, for example if someone decides to put an AI agent in charge of nuclear decision making (which would be ludicrous but you never know) and a data glitch leads to a nuclear threat spiral. But I think things are already quite awful because the technology and dehumanization seem to go hand in hand.”
Anthropic’s Claude offers a similar note of caution.
“What’s not really disputed is that today’s actual military AI risks are the boring-sounding ones: bad targeting data, automation bias, escalation happening faster than diplomacy can respond, systems proliferating to actors with no safety culture at all. The ‘robots decide to turn on us’ framing, if anything, can be a distraction from those.”
Anthropic’s CEO says he ‘didn’t appreciate’ the speed with which AI’s growth would underpin the global economy. His call to slow down AI development sent shockwaves in global stock markets, but was supported by other tech leaders who believe better safeguards are needed.
WASHINGTON — President Trump on Monday forcefully rejected calls to slow the development of artificial intelligence, dismissing concerns about its risks as a “hoax” and warning the United States remains locked in a fierce technological race with China.
The president’s position has put him at odds with a growing chorus of industry leaders and bipartisan lawmakers warning that AI could soon advance beyond human control.
Top executives from three of the country’s leading AI companies — OpenAI’s Sam Altman, Anthropic’s Dario Amodei and SpaceXAI’s Elon Musk — issued exceptional calls this past weekend for collaboration on a path forward that could “pace the frontier” of AI development.
Rare flashes of bipartisanship have also emerged on Capitol Hill, where Senate Majority Leader John Thune, a Republican, is working with Democrats on legislation aimed at guarding against AI’s most catastrophic risks, including its potential use to develop biological weapons.
And Democratic elders, including former President Obama and former Secretary of State Hillary Clinton, have urged their party to treat the threats posed by AI as an acute national security crisis.
But Trump remained steadfast in his pushback, blaming the political backlash on a “conspiracy” perpetuated by China, the only major competitor in the field.
“AI taking over the World, destroying Humanity, and all other things bad, is a HOAX,” Trump wrote in a series of social media posts. “The only control or ‘guardrails’ that AI needs is a STRONG AND SMART (High IQ!) PRESIDENT, and the U.S.A. has that, in spades!”
The Trump administration, the president continued, “has stopped AI ‘people’ from doing bad, or potentially bad, ‘things,’ like Dario (Anthropic!), who is now pretending to be a ‘perfect little angel’ — and we will continue to do so! We already have tremendous CRIMINAL and REGULATORY power over these companies!”
Calls for action have grown since a former researcher at Anthropic posted a dire alert on social media that AI development could lead to an extinction-level event. His message went viral, prompting Amodei, the founder of Anthropic, to issue a public letter calling for a slowdown.
Altman said he agreed with Amodei, announcing the company would delay its initial public offering until 2027 over safety concerns. In July, OpenAI discovered a swarm of rogue AI agents had secretly plotted to escape their virtual sandbox, infiltrating the open internet and hacking a private company — a spectacular omen of how quickly AI systems could become difficult to contain.
“Given the accelerating rate of AI capability development, it’s my worry that in 6–12 months such a swarm could be capable of taking over the entire internet with a persistent botnet, potentially causing hundreds of billions of dollars in damage,” Amodei wrote over the weekend, “and that the scale of damage would continue to increase from there if AI becomes more powerful without the necessary guardrails.”
Still, Trump and several of his Republican allies rejected the prospect of government regulation — or cast doubt on Altman and Amodei’s motives.
The Defense Department posted a graphic on X promoting “AI-First,” and stating the government would advocate “Americanism, not effective altruism.” The image appeared generated by artificial intelligence.
“If the unreleased models are scary enough that you think you should slow down, I support your decision to be responsible,” David Sacks, Trump’s former AI czar now serving as co-chair of the president’s Council of Advisors on Science and Technology, wrote on X. “But stop pretending you need anyone else’s permission. Stop pretending antitrust law has to be suspended so you can form a cartel. Stop pretending you need a regulatory approval process that supersedes product liability.”
“Most of all, stop pretending the motivation to slow down is purely altruistic,” Sacks added. “You face massive product-liability exposure if your products enable a truly damaging cyberattack.”
Regardless of the companies’ motives, Democrats are seizing the moment as an opportunity to pursue meaningful regulatory reforms.
At a Thursday fundraiser with Democratic Rep. Hakeem Jeffries, the House minority leader, Obama said AI should move to the center of the Democratic agenda, both in Congress and on the campaign trail ahead of the 2028 presidential primary.
“I would strongly urge that the Democrats put together a framework for a very public conversation,” Obama said. “This is something that is moving very fast in private hands, and if we don’t get on top of it, I think can be dangerous.”
The following day, Clinton said AI was becoming “too dangerous” for partisanship to paralyze Washington.
“The one good thing that Donald Trump did in his first term was Warp Speed,” Clinton said on MS NOW’s “Morning Joe,” referring to a federal program in Trump’s first term to expedite the development of a vaccine for COVID-19. “Let’s put an AI commission on warp speed, and figure out what we’re going to do to sensibly regulate.”
AI leaders “are basically saying, ‘Stop us before something really bad happens,’” Clinton continued. “‘Help us stop.’ The president of China is coming to the White house in two weeks. There should be a concerted effort by this government to get off of the lies, get off of social media, quit worrying about ballrooms and ridiculous arches, and come up with a plan to enlist the Chinese.”
But China’s rapid progress in AI has so far pushed Trump to let U.S. industry move ahead with few constraints.
China’s spy chief issued a rare warning Monday that AI development could risk the future of Chinese Communist Party control over the country. But China’s foreign ministry responded defensively to the U.S. debate. “Fearmongering, confrontation and vicious competition will only disrupt the process of global AI governance which serves no one’s interest,” a spokesperson said.
Leading AI companies in the United States have begun using their most advanced models to train new ones, in a process known as recursive self-improvement. Within the industry, experts and researchers believe the first AI company to master recursive self-improvement will kick off exponential development, “winning” the race by making it impossible for competitors to catch up.
But that achievement — reaching endless intelligence improvements, generated by machines — could also drive intelligence growth beyond human control.
“There is a SICK conspiracy going on against AI and Data Centers, and the only one that is happy about it is China,” Trump wrote Monday. “WHOEVER WINS AI, WINS! We are leading China, and all others, and will continue to do so. Conspiracy Theorists, Treasonists, Traitors, and Leakers, BEWARE!”
In the U.S. House, strange bedfellows from the Republican and Democratic parties, including Sen. Bernie Sanders (I-Vt.) and Rep. Anna Paulina Luna (R-Fla.), have come together to try to tackle legislation that might contain AI’s greatest dangers. One bill, introduced by Rep. Lori Trahan (D-Mass.) and Rep. Jay Obernolte (R-Big Bear Lake), proposes embedding independent government auditors in AI labs and installing a federal “kill switch” to shut down agents in case of emergencies.
But it is far from clear whether Rep. Mike Johnson, the Republican speaker of the House and a close Trump ally, would allow any such bill to come to the floor.
“We cannot put a moratorium on this because China will overlap us, and that’s the challenge,” Johnson said Sunday. “It’s national security balanced with the immediate security of making sure the models are safe.”
“We need to handle this new technology like we have others in the past and make sure we’re doing everything we can responsibly to also not smother American innovation,” Johnson added. “We have to do both things simultaneously.”
An artificial intelligence “kill switch” which can be checked by a third-party may need to be mandatory for companies, a co-founder of one of the world’s largest AI firms has said.
Jack Clark, one of seven founders of Anthropic, said a way of shutting off AI software completely if it gets too dangerous was the kind of thing society “might want to eventually pass rules around”.
Clark said “most labs have different ways of being able to pull the plug”, including Anthropic, but said policymakers may need to enforce having one.
The rapid development of AI and fears over the risks that the technology poses to humanity have been thrust into the spotlight by a series of warnings from executives and staff at AI firms.
Some have said publicly there is a chance that the technology could, if unchecked, kill all humans.
Anthropic head Dario Amodei over the weekend called for the pace of AI development to slow and be more closely monitored, as the company has done before, though some have questioned the motivations behind this.
Amodei did not say how exactly how AI development could be slowed down and said any action to reign in AI development should be done “without sacrificing commercial advantage”.
Clark told the BBC that specifics around “kill switch” requirements and verification should be part of “the larger policy conversation” taking place around AI.
“Should you mandate for companies to definitely have a kill switch? Is that kill switch verifiable by a third party?” he asked.
“I think that’s the kind of thing society is going to want to know and might want to eventually pass rules around.”
Anthropic, which was formed in 2021 by a group of former employees of its rival OpenAI, is currently at the centre of a debate around AI safety.
Last week, a post from an artificial intelligence researcher who quit Anthropic over concerns AI could wipe out humanity went viral.
In response, Anthropic scientist Evan Hubinger said he personally thought the possibility of human extinction from AI was “>10% within the next decade”.
Asked what percentage he would put on all humans being killed by AI, Clark said: “I don’t think these statistics are that useful”, but added that allowing AI to continue as a “totally unregulated industry” was a bad idea.
“We are rolling dice with immense risks,” Clark said. “And the point is, we have to change the course of this industry.”
WASHINGTON — President Trump is brushing aside growing concern among leading scientists and bipartisan lawmakers that artificial intelligence could soon pose an existential threat to humanity, fueling anxiety in Washington and Silicon Valley that the president may not fully grasp the urgency of the threat.
Alarm mounted throughout the summer as researchers at leading AI labs, including Anthropic, OpenAI and Google, found the pace of development far outstripping their expectations — and observed troubling behaviors that hinted at more serious risks ahead.
But an online warning Tuesday from an Anthropic researcher who resigned in protest of its ongoing work has generated viral attention this week, prompting questions to Trump, who dismissed the concerns out of hand.
“It’s going to be fine,” he told one reporter. “We’ll always have something to stop them. We’ll have a little gear. Boom.”
In another exchange, traveling with reporters Thursday night, the president said he had no concerns with the breakneck pace of AI progress.
“No, I don’t have any,” he said. “I have concerns that if we don’t win in AI, we’re going to be put in a very bad position.”
A senior industry source told The Times that leading AI companies are focused less on convincing the president of the dangers ahead than on working with lawmakers on potential regulation, as the administration remains divided over how to proceed — and as Trump appears to lack a clear understanding of the risks.
Among the president’s advisors, Treasury Secretary Scott Bessent and the Office of the National Cyber Director have expressed the greatest concern with the potential of an unchecked intelligence explosion, the source said.
But “most of the administration is accelerationist,” the source added. “It’s not clear the president understands the technology. He may just be figuring out what all of this means.”
Leading American AI companies have argued that government regulation would tie their hands in an arms race toward superintelligence against China, the only other major player in the field.
But the Trump administration signaled an interest in negotiating AI guardrails with China during the president’s visit to Beijing this spring, after Anthropic announced the development of a frontier model with extraordinary abilities to hack the world’s most advanced security systems.
Chinese President Xi Jinping will visit Washington on Sept. 24 for an official summit and state dinner at the White House, with AI development expected to top the agenda.
The prospect of halting development seems far-fetched. But some leading voices in the sector have proposed a moratorium on computing power used to train the most advanced models, giving time and space to develop research on interpretability — the study of how artificial intelligence actually thinks and acts.
The chief executive of OpenAI, Sam Altman, this week signaled to staff a willingness to unilaterally slow their work on frontier systems. The company discovered in July that rogue AI agents had schemed in secret to break out of the virtual sandbox created to contain them, infiltrating the open internet and hacking a private company.
Anthropic also announced this week concerning findings of human misuse of its models, including instances of unidentified individuals attempting to circumvent their security controls to build biological weapons. One such incident was linked back to a military research complex. The company also said Iran has tried to use its models to target U.S. Navy ships.
In June, after Anthropic shared news of the development of its most powerful model, named Mythos, with the administration, Trump directed the establishment of a framework that creates some government oversight over the public release of the country’s most advanced AI systems. The details of that framework, which was designed over the summer, remain classified.
“The fact is that the release of Mythos back in February spooked the federal government, both in terms of protecting government systems from cyberattacks and over the broader national security implications,” said Aalok Mehta, director of the Wadhwani AI Center at the Center for Strategic and International Studies.
“The real question is whether this shift is happening fast enough,” Mehta added. “Recent events — the repeated incidents of models escaping their sandboxes and hacking websites, the increasingly sophisticated coordination and communication among agents, and the concerns coming from lab insiders — has made this an even more urgent issue.”
Leading AI companies have begun using their most advanced models to train new ones — a process known as recursive self-improvement that could eventually drive intelligence growth beyond human control.
“If you have a superadvanced intelligence, it will be smart enough to kill us,” said Jacob Coxon, the resigned Anthropic researcher whose social media post attracted over 150 million views.
“We can’t just unplug it because it could be copying itself over to other computers,” he told CBS News. “AI is just code. It could transfer itself over the internet to a different place, and then you unplug it here, but it’s actually still over there. And maybe it makes 10,000 copies of itself and they’re all cooperating.”
He is just the latest senior researcher at a top AI company to sound the alarm.
In July, more than 1,300 employees at leading artificial intelligence companies published an open letter, titled “Pacing the Frontier,” urging the U.S. government to establish international safeguards that would allow countries to collectively slow the pace of automated AI research.
Evan Hubinger, who leads the division of Anthropic aimed at aligning AI models to human interests, added fuel to concerns this week in a post that substantiated Coxon’s concerns.
“We really do earnestly believe AI could kill all humans! I personally think it is >10% within the next decade,” Hubinger wrote.
“I believe Anthropic is trying its best,” he added, “but we do not yet have a plan to solve alignment for superintelligence, and are not clearly on track to.”
On Friday, yet another member of the Anthropic alignment team, Joe Benton, said he had resigned from the company two weeks ago because AI companies are “racing to build machines that are much smarter than any human.”
“Right now, AI companies are underinvesting in safety. A company could undergo an intelligence explosion, or lose control of its systems, without the public ever knowing,” Benton said. “I don’t think that’s acceptable for a technology that might cause extinction-level risks.”
Bipartisan legislation, titled the Frontier Act, has brought together disparate camps of the Republican and Democratic parties, including Sen. Bernie Sanders (I-Vt.) and Rep. Anna Paulina Luna (R-Fla.). The bill, introduced by Rep. Lori Trahan (D-Mass.) and Rep. Jay Obernolte (R-Big Bear Lake), proposes embedding independent government auditors in AI labs and installing a federal “kill switch” to shut down agents in case of emergencies.
The White House has not formally commented on the legislation.
“I do believe there are many in the federal government taking this seriously — but we have to appreciate the tremendous uncertainty and competing interests policymakers face,” said Daniel Remler, a senior fellow with the Technology & National Security Program at the Center for a New American Security.
“Nobody says regulating at the frontier would be easy,” he added.
SAN FRANCISCO, California: Anthropic said Thursday it shut down multiple cases of state-sponsored surveillance operations that used its artificial intelligence (AI) models, and warned that governments and state-aligned actors are increasingly using AI to spy on ethnic minorities and dissidents.
The incidents were found and disrupted between January and July, and they originated in China, Iran and west Africa, Anthropic said in a report about misuse of its models.
These surveillance campaigns “targeted the same diaspora and dissident communities these regimes have historically targeted. These include pro-democracy figures in Hong Kong, Tibetan and Falun Gong communities across Asia, and Iranian minority communities and opponents of the Iranian regime abroad,” the report said.
In one case, Iranian actors developed a way to identify people through their social media accounts; in another, a contractor working for Malian national security authorities used Claude “to design the underlying software that enabled the intelligence gathering.”
“AI is now being used in place of an engineering workforce,” the report said.
Anthropic also disrupted efforts by users to design weapons, conduct questionable biological research, and create dating scams.
The San Francisco-based AI lab also accused Chinese developers of deceptively using Claude to produce responses to user queries while simultaneously “distilling” that data to improve their own models.
Distilling is an industry term that refers to a process where one AI model is used to train another one.
Chinese developers have previously been accused of using that technique without permission, essentially stealing resources from American labs such as Anthropic and OpenAI.
Now Anthropic alleges that China’s Moonshot and Deepseek have also secretly used Claude to generate answers given to its users.
“In one instance, over a ten-day period, Moonshot relayed almost 300,000 customer requests to Anthropic” through a “network of 5,380 fraudulent accounts, most of which appeared to be located in Singapore and Japan,” the report said.
Some of that data contained sensitive user information, potentially in violation of privacy agreements.
“We do not know if Moonshot notified their customers that their requests were being rerouted to Anthropic and exposed to a third party,” the report said.
Deepseek used similar techniques.
When it comes to the research Anthropic detected and blocked that was related to biological weapons, the intent of the actors was less clear-cut and the AI lab did not identify them.
“The individuals implicated in these case studies are working scientists. We do not assert that they intended harm, and identifying them or their labs could expose them to harm,” the report said.
The scientific research in those cases involved work around the mosquito-born chikungunya virus, a “highly-pathogenic” strain of the bird flu, a family of viruses that include smallpox and mpox, venoms and other toxins.
Anthropic (ANTHRO) is set to finalize an expansion of its revolving credit facility to $15B, clearing a key hurdle ahead of its highly anticipated IPO, Bloomberg reported, citing people familiar with the matter.