hackers

French fridge fright: Why supermarkets have become target for hackers | Cybercrime News

Hundreds of French supermarkets have suffered unprecedented cyberattacks resulting in tonnes of food perishing and raising fears about the vulnerabilities of food systems to advanced technology.

The attacks, which appeared to target internet-linked refrigeration systems manufactured by a Danish company, raised the temperature of fridges and freezers to as high as 50 degrees Celsius (122F) at more than 500 shops and supermarkets across the country. Supermarkets confirmed the attacks on Monday.

Recommended Stories

list of 4 itemsend of list

France’s cybersecurity agency has advised companies operating affected freezer models to immediately disconnect them from the internet – or restrict access to them – and to perform software updates.

It is unclear who may have been behind the attacks, but authorities say they have now launched an investigation.

Here’s what we know:

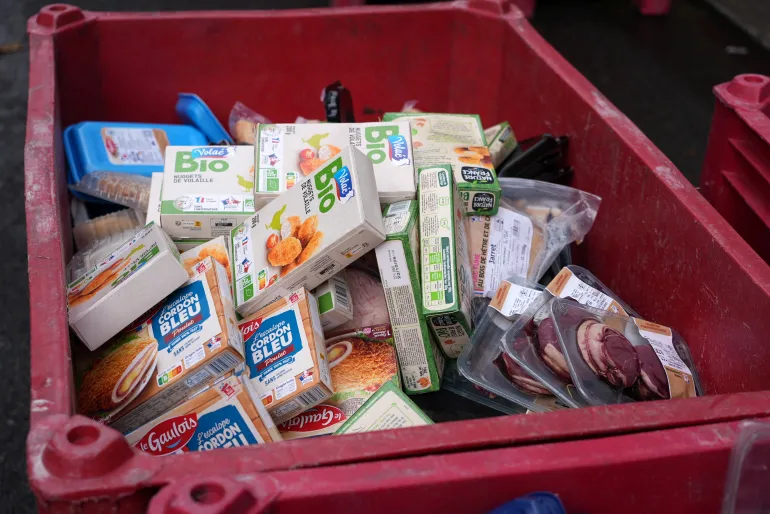
Perished goods outside a supermarket in Paris the day after a cyberattack targeted refrigeration systems in France, October 13, 2026
Perished goods outside a supermarket in Paris the day after a cyberattack targeted refrigeration systems in France, October 13, 2026 [Lucien Libert/Reuters]

What happened?

Hackers gained internet access to the refrigeration systems and remotely cranked up temperatures in freezers and fridges to 50C during the night when shops were closed. Millions of euros worth of food was spoiled, according to retailers. In some cases, the raised temperatures sparked fires or melted equipment.

French supermarket groups E-Leclerc, Intermarche, Carrefour, Monoprix and Cooperative U were all hit.

At least 300 of Intermarche’s stores and its Netto brand were affected. Cooperative U said more than 100 of its supermarkets were targeted, while Carrefour said 80 supermarkets were affected and Monoprix reported that about 5 percent of its roughly 490 stores were hit.

Officials are still investigating who launched the attack and how it was carried out. French TV channel BFM reported that the attackers appeared to have remotely triggered a forced defrosting option in the refrigeration systems.

The systems targeted are built by Danish manufacturer Danfoss, according to France’s government cybersecurity agency. The refrigeration models attacked included the AK-SM800 and AK-SC355.

Danfoss told the AFP news agency that most of the affected control systems were “legacy” products that had “outdated firmware”. The company said it had previously advised supermarkets to update them.

AFP also reported that officials are liaising with other European countries which may have been affected.

It is unclear exactly how much food has been lost. The attacks come after President Emmanuel Macron ordered last month that the country’s critical infrastructure be protected from Russian “hybrid attacks”.

Have supermarkets been hit by cyberattacks before?

Yes. Attacks like these have been reported in other parts of Europe and in the United States.

In April 2025, British retailer and supermarket chain Marks and Spencer suffered a sophisticated ransomware attack that the company said cost it approximately 300 million pounds ($397m) after it was forced to suspend online and app orders. The attack was orchestrated by a hacker group called Scattered Spider, using ransomware from DragonForce, another criminal group. Ransomware attacks involve using malicious software to hide essential data unless a ransom is paid.

According to UK media, the same hackers also tried to attack Co-op and the iconic Knightsbridge store, Harrods.

Similar reports have also emerged from the US. In June 2025, United Natural Foods, a frozen food company which supplies big supermarket brands such as Whole Foods, said it had discovered a cyberattack that forced it to take its systems offline. The company did not reveal the nature of the attack.

In November last year, Ahold Delhaize USA said it was the victim of a cyberattack that disrupted operations at more than 2,000 stores, including Hannaford, Food Lion and Stop and Shop.

Why target supermarkets?

They are an easy target and the consequences can be widespread.

As food and agricultural systems increasingly digitise, analysts say supermarkets selling perishable foods are increasingly vulnerable to attacks due to the nature of their stocks.

The rising sophistication of cyberattacks now means that common people and local, third-party companies relying on big chains for business are also falling victim as attacks disrupt supply chains, experts say.

Speaking to Al Jazeera, tech and cybersecurity analyst Steven Lachance said smart appliances connected to the internet will always be vulnerable as hackers seize on security lapses to log in to the systems remotely and trigger malicious features.

“It’s the new reality of having these connected equipment,” Lachance said, pointing out that attacks could evolve to target medical or energy systems.

“This should come as a global wake-up call … Throughout society, we have connected infrastructure that is live on the internet, and that can be hacked. It’s a new reality, and we absolutely need national and international measures to prevent those attacks; otherwise, it’s just going to keep happening,” he warned.
Source link

Chinese hackers impersonated AI experts to target US policy minds | Cybersecurity News

TA419 hackers used deceptive tactics, impersonating real figures like a former White House AI official

Chinese hackers have been impersonating artificial intelligence (AI) experts in the United States, including a former government official, according to a new report from cybersecurity firm Proofpoint.

The report, released on Thursday, found that in July, a China-aligned hacking group called TA419 targeted a slate of US policy experts by impersonating prominent figures, including Lynne Edwards Parker, the former principal deputy director of the White House Office of Science and Technology Policy.

Recommended Stories

list of 4 itemsend of list

The hackers, who had been operating since April 2025, first sent otherwise harmless-looking emails intended to engage a target, such as requests to join an “AI Policy Advisory Committee”, and, once they responded, the target would be sent to a fake login page designed to steal their credentials.

The targets included policy experts at think tanks, defence contractors, universities and law firms in both the US and Japan.

The report used a technique that creates a fake browser pop-up window inside a legitimate webpage that mimics an authentic-looking sign-in prompt to deceive victims and make it harder for them to realise they are handing over their information to hackers.

Proofpoint did not specifically name the targets hacked, but the Reuters news agency was able to confirm at least one of them as Alex Engler, a former White House official who now heads the Penn Center on Media, Technology, and Democracy.

Engler told Reuters that he got one of the emails, but after checking with industry colleagues, he discovered that he had received the email from an impersonator.

In February, the same group was behind the impersonation of a “prominent” Anthropic employee in efforts to target AI policy experts. The cybersecurity firm behind the report believes that the group will continue to target think tanks and other policy experts and will continue to use the identity of real-world experts to do it.

Parker did not respond to Al Jazeera’s request for comment.

Source link

FBI says investigating breach of ‘very sensitive’ data by hackers | Donald Trump News

Hacker group ShinyHunters claims to have detailed data on thousands of FBI employees.

The United States Federal Bureau of Investigation says it is investigating a breach of its jobs website by a hacking group that claims to have obtained sensitive data on thousands of employees.

“The FBI is aware of a cybercriminal enterprise group claiming a compromise of the fbijobs.gov portal and alleged impact to FBI employee personally identifiable information,” the agency said in a statement on Wednesday.

Recommended Stories

list of 3 itemsend of list

“While the point of breach is still undetermined — whether a third -party or the FBI’s enterprise — we are actively and aggressively investigating this matter and working closely with those third-party providers that support fbijobs.gov to mitigate any and all risk.”

Several news outlets, including Reuters news agency, reported they had seen parts of the data, claimed to be part of a larger trove between two and three terabytes by ShinyHunters, a hacking group claiming responsibility for the breach. According to Reuters, the data includes granular detail about scores of bureau officials’s job assignments, including sensitive work against Chinese spies, Russian intelligence, drug cartels and more.

ShinyHunters said on Tuesday that it had breached the FBI and stolen data on a huge number of current and former FBI employees. ⁠⁠It said it is holding the data hostage until the bureau rescinds an unflattering statement about the group issued in May. On Wednesday, the group said it was trying to keep the ⁠⁠personnel information from circulating widely in the meantime.

An FBI statement in May characterised ShinyHunters as “threat actors” who often harass or threaten victims, using “their real or exaggerated claims of access to sensitive or personal information to prompt payment from victims”.

The group “may falsely claim to have sensitive or compromising information, including embarrassing photographs or videos of victims, which frequently do not exist,” the FBI said.

The FBI has been a common hacking target.

In March, the FBI disclosed that it was investigating “suspicious activities” on an internal system that contains sensitive information related to surveillance operations and investigations. Also that month, a pro-Iranian hacking group claimed to have hacked an account of FBI Director Kash Patel and posted online what appear to be years-old photographs of him, along with a work resume and other personal documents dating back more than a decade.

The jobs portal was still offline Wednesday afternoon.

Source link