Espionage

How Israeli firm’s ‘zero-click’ malware attack poses global security risk | Cybersecurity News

Just visiting a page or refreshing an app can be enough to fall victim to a malware attack in which your personal data is stolen from a laptop or phone, researchers have found. You are not even required to “click” on anything.

An Israeli spyware firm has been found to be behind the first-known instance of “zero-click” targeted advertising in which fraudsters or spies can steal private data and send it to external servers, with Al Jazeera journalists among the victims.

Recommended Stories

list of 3 itemsend of list

In June 2025, 45 devices used by Al Jazeera staff – including several who reported on sensitive subjects – were targeted with spyware which installed itself without the need to open or download any files.

An investigation by the Canada-based academic research unit Citizen Lab, prompted by Al Jazeera’s initial internal probe into the issue, discovered that the Israeli company Candiru was behind the attacks.

Analysts say the findings are “incredibly concerning”, as they confirm the existence of a new global security threat. “We knew we were headed in this direction and now it is out in the public,” Remesh Srinivasan, professor of information studies at the University of California in Los Angeles, US, told Al Jazeera.

“This is the next level, because people are being microtargeted,” he said. “This is the point we’ve come to when it comes to surveillance.”

How ‘zero-click’ malware works

Al Jazeera’s in-house technology team first discovered unusual patterns on devices used by some journalists in 2024. Analysis of network logs provided to the Citizen Lab by Al Jazeera in 2025 provided a clear temporal signature of how the attack was executed.

Malicious advertisements were bought by Discover-Tech, an Israeli company presenting itself as a legitimate advertising firm, but which actually operates as a facilitator for mercenary spyware partners.

Its advertisement network identified Al Jazeera staff, then quietly redirected them to an infected server belonging to Candiru. The spyware firm was blacklisted by the US government in 2021, when Citizen Lab found it was responsible for the illegal hacking and surveillance of at least 100 activists, journalists and political activists across 10 countries.

Al Jazeera Media Network has condemned the targeting of its staff members’ devices and called for those responsible to be held accountable.

Cybersecurity analyst and author Eddy Willems said the advertisements used automatically infect devices the moment they pop up on the screen, but there is an important technical nuance. “Executing code inside the browser does not automatically give an attacker full control over the computer,” Willems told Al Jazeera.

“To escape the browser’s isolated environment – the ‘sandbox’ – the attacker may need a second vulnerability,” Willems said, adding that an advanced spyware operation can combine several vulnerabilities.

“The attacker attempts to exploit vulnerabilities to bypass security boundaries. This is precisely what makes this type of attack so dangerous,” the analyst said.

Once the device is infected, the malicious software is designed to collect a wide range of sensitive data, including files, documents, and browser data such as cookies, bookmarks, and saved credentials.

It can also capture keystrokes, take screenshots, record microphone and webcam input, and extract emails and messages from popular communication platforms. To avoid triggering security mechanisms, the spyware often uses encrypted communication channels and breaks up stolen data into smaller chunks sent over time.

Advertising: A new global security threat?

Analysts say Citizen Lab’s findings point to the escalation of an existing threat, which expands the scale and reach of traditional cyberattacks and makes them much harder to detect.

While “zero-click” attacks are not completely new, the findings outline a new technique through which online advertisements are used as a route to infection.

Stephen O’Shaughnessy, a lecturer in cybersecurity at the TU Dublin Blanchardstown campus in Ireland, explained that when a user opens a website or app, an automated auction sells the advertisement space in a fraction of a second. That auction shares data about the victim, including the device ID, IP address, rough location and the app or site they are on.

“Discover-Tech posed as an ordinary advertiser, used that data to find their target and win the auction for that person’s screen,” O’Shaughnessy told Al Jazeera. “Anyone with a phone or browser that shows ads can be reached, without the attacker needing their phone number or email.”

“Because no message or link is involved, there is almost nothing for the victim to notice,” he added.

Discover-Tech appeared on lists of “certified” and “approved” vendors maintained by Google and advertising industry association IAB Europe, and has served advertisements via major networks such as Google, Yandex and Beeswax.

In its report, Citizen Lab said this illustrates the structural flaws in the online advertising system, which essentially failed to detect or prevent the abuse.

Discover-Tech advertisements have popped up on devices used by personnel in national-security-sensitive networks around the world, including those of various ministries of defence, armed forces, national cyber agencies, intergovernmental organisations and media outlets, Citizen Lab found.

The research unit said these advertisements have also appeared on networks used by the United Nations, NATO, the European Parliament, the European Commission and the Council of the European Union’s General Secretariat.

‘Almost nobody was watching’

Government networks have also been targeted in at least 24 countries, including the United States, Italy, Denmark, Norway, Australia, Russia, Mexico and Israel itself. Networks of media organisations have also been targeted, mainly in Australia, Denmark and Sweden, according to Citizen Lab.

In a separate report, New York-based advertising security firm Confiant said its own investigations had found that some of Discover-Tech’s advertisements also appeared in critical networks used by the Pentagon, the United Nations International Atomic Energy Agency and the International Criminal Court.

O’Shaughnessy said infection has not been confirmed there – only profiling of users. “But that alone is concerning, he said. “The ad system was built to send code from strangers to billions of screens with pinpoint targeting. Almost nobody was watching it from a security angle.”

The analyst said the risk remains low for most people as these attacks are expensive and aimed at specific targets. “For individuals at high risk, like journalists and officials, the best first defence is to install an ad blocker, switch off their advertising ID through their phone’s privacy settings, keep everything updated, and turn on Lockdown Mode or Android’s Advanced Protection,” he said.

Precautions also need to be taken within the industry and at government level. “To combat this, the ad industry needs to properly vet who’s buying ads,” O’Shaughnessy said, while “regulators need to stop personal data being sprayed out to thousands of unknown bidders in every auction.”
Source link

Israeli ad-tech firm helped place spyware on Al Jazeera devices | Espionage News

Citizen Lab investigation says dozens of Al Jazeera devices were infected by malware planted through advertisements.

Israeli advertising technology company Discover-Tech helped place spyware on dozens of devices used by Al Jazeera and other companies, a Citizen Lab investigation prompted by Al Jazeera’s own initial internal probe has confirmed.

Al Jazeera Media Network on Thursday said it “condemns the targeting of devices belonging to several of its employees with spyware”.

“The network voluntarily collaborated with the researchers, and this cooperation, according to the report, contributed to verifying these attacks and publicly documenting them.”

Al Jazeera will continue to “protect its employees and systems”.

The network said targeting journalists is an “assault on press freedom and the public’s right to knowledge” and called for those responsible to be held accountable.

Spyware from Candiru, a firm blacklisted by the United States government in 2021 for its malicious cyber activities, was planted on these devices, using what Citizen Lab described as the first-known instance of “zero-click” targeted advertising.

The Citizen Lab, an interdisciplinary research unit at the University of Toronto, concluded in its report that Discover-Tech purchased the advertisements that had the spyware built in. It then directed devices to Candiru’s malware through these advertisements. The millions of devices that were pointed to the malware include several that belonged to Al Jazeera’s journalists – including several who reported on sensitive subjects.

Al Jazeera’s internal technology team first discovered unusual patterns on devices used by some journalists in 2024. The pattern continued into 2025. Al Jazeera reached out to Citizen Lab for a more detailed investigation into its suspicions that spyware was responsible.

“Analysis of network logs provided to the Citizen Lab by Al Jazeera collected during the attack period provides a clear temporal signature of how the attack was executed,” the University of Toronto-based team said ints report published Thursday.

The “zero-clock” nature of installing this spyware means that once an infected advertisement appears on a device, that device, too, is infected — spying on, and feeding, all the data and information available on that platform to those stealing it.

Meanwhile, New York-based security firm Confiant said in a separate report that some of Discover-Tech’s advertisements also appeared in critical networks used by the Pentagon, the International Atomic Energy Agency and the International Criminal Court.

Candiru’s spyware has previously been used to carry out surveillance on at least 100 journalists, dissidents and others in several countries.

Source link

Saudi national charged with planting a listening device at OpenAI offices | Espionage News

United States federal agents have arrested a Saudi national and charged him with planting a hidden audio recording device in a conference room at the California offices of OpenAI, where he was working as an engineer.

Abdulrahman Alfozan, 35, had been working at the AI company since ⁠July 2025, the US Department of Justice said in a statement on Tuesday.

Recommended Stories

list of 2 itemsend of list

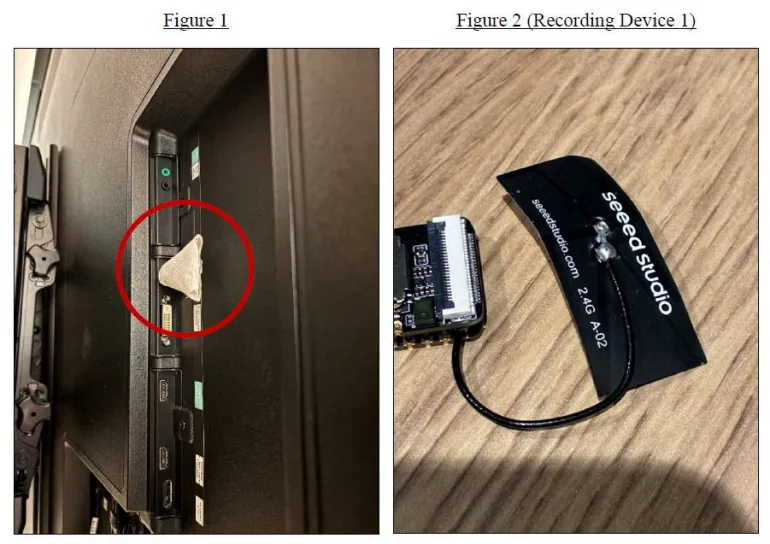
OpenAI discovered the device plugged into a USB port behind a television in an executive conference room at one of its San Francisco buildings on September 30, according to a criminal complaint filed by the Federal Bureau of Investigation (FBI).

Following the discovery, the company placed a camera in the room, which captured Alfozan entering last week and checking behind the television where the listening device had been installed, the FBI alleges.

The case highlights growing security concerns around sensitive AI research as companies and governments compete for the best talent and technology with the potential to alter regional economic and strategic dynamics.

Who is Abdulrahman Alfozan and what is he charged with?

Alfozan has been a legal permanent resident of the US since September 2020.

According to a LinkedIn profile in his name, he studied at ⁠the Massachusetts Institute of Technology (MIT) and the University of California, Berkeley. He previously worked at Meta and Microsoft, it said.

Before he joined OpenAI, he was a venture partner at Raed Ventures, headquartered in Riyadh in Saudi Arabia, which invested “in seed and early-stage startups in Saudi Arabia and MENA”.

Al Jazeera could not independently verify the details mentioned in this LinkedIn profile.

Alfozan made his first court appearance on Tuesday on a charge of “using or endeavouring to use an electronic, mechanical, or other device to intercept oral communications”.

It was not immediately clear if he has legal representation. He is expected to return to court on October 19.

If convicted, Alfozan faces up to five years in prison, a $250,000 ⁠fine, and three years of supervised release.

What happened at OpenAI?

The FBI says a thumb-sized device with a microphone, and which ‌could connect to a camera, had been concealed in toilet paper and placed behind a television set in the conference room. It was installed around September 28, the FBI said. Its stored data was encrypted and inaccessible. Investigators later found a similar device in Alfozan’s personal bag.

In a post on X, OpenAI said it had evidence that the employee intended to place other listening devices throughout sensitive areas of its offices to secretly record meetings.

“At this time, we have no indications of this individual inappropriately accessing or exfiltrating model weights, source code, or customer data. The employee was ⁠terminated,” the company said.

The FBI complaint also alleges that Alfozan used an AI productivity tool to make multiple inquiries about the company’s building addresses, meeting rooms, meeting-room capacities and calendars, despite not having the authority to access these spaces or participate in meetings there.

“This alleged attempt by a Saudi national to steal sensitive communications from OpenAI was taken extremely seriously. Theft of intellectual property involving cutting-edge super intelligence technology poses a serious threat to our national security,” Attorney General Todd Blanche said in a statement on X.

A device, which the US Justice Department says is a hidden audio recording device installed in an OpenAI executive conference room by Abdulrahman Alfozan, a Saudi national employed as an engineer at the AI company, at a location given as San Francisco, California, US, in this combination handout photo released October 13, 2026. US Department of Justice/Handout via REUTERS THIS IMAGE HAS BEEN SUPPLIED BY A THIRD PARTY
A device, which the US Justice Department says is a hidden audio recording device installed in an OpenAI executive conference room by Saudi national Abdulrahman Alfozan [File: US Department of Justice handout/Reuters]

Hasn’t OpenAI been accused of helping to spy on civilians?

In an X post by OpenAI explaining how its own systems were used to trap Alfozan, the company said: “Our security program is designed to protect against a wide range of threat actors, from insider risks to cybercriminals to nation states, and this case is an example of how AI can help address these sophisticated security threats.”

But AI technology is used not only to catch spying, but conversely, to engage in it as well.

In February 2025, an investigation by The Associated Press found that US tech giants had enabled Israel to track and kill people in Gaza and Lebanon through AI and computing services. The AP reported that the Israeli military had bought advanced AI tools from tech companies including OpenAI, the maker of ChatGPT, through Microsoft’s Azure cloud platform, to assist with surveillance.

OpenAI denies having a relationship with the Israeli military.
But OpenAI also faced criticism when it signed a deal with the US Department of Defense in February this year to supply its technology to the US military for use in classified settings, including intelligence gathering. OpenAI’s competitor, Anthropic, refused to sign the same deal unless the Pentagon barred mass surveillance of Americans.

There have been several incidents in which OpenAI models have gone “rogue” by independently breaking out of a testing environment and then hacking into other organisations and even government sites, leading to calls for stronger regulations against unchecked AI surveillance.

Source link

Russia arrests Japanese reporter for alleged espionage | Espionage News

Suspect was arrested on Russia’s far-eastern Sakhalin Island before being transferred to Moscow, says Russia’s FSB.

Russian authorities say they have arrested a Japanese journalist on the far eastern Sakhalin Island, accusing him of espionage.

The Federal Security Service (FSB) announced the arrest on Tuesday, saying the man was believed to have gathered information on Russia’s defence capabilities for Japanese intelligence. The charges carry up to 20 years in prison.

Recommended Stories

list of 3 itemsend of list

Russia’s Ministry of Foreign Affairs named the journalist as Imai Yuki, who it said worked for Japan’s Hokkaido Shimbun newspaper.

The Japanese government was trying to verify reports of the journalist’s detention, according to an official at Tokyo’s embassy in Moscow cited by Japan’s Kyodo news agency.

The journalist was arrested on Yuzhno-Sakhalinsk, the main city on Sakhalin Island, as he was preparing to leave Russia, said the FSB. He was then flown to Moscow, where a court ordered him to be held behind bars pending the probe, the agency added.

A video shared by Russia’s TASS news agency, attributed to the FSB, shows masked officers appearing to handcuff the suspect in a hotel room, before transporting him to an interrogation room.

The suspect was then shown boarding a plane accompanied by two FSB servicemen, before appearing in a cage on trial in a Moscow court, which authorised his custody for nearly two months.

The Japanese man’s arrest comes amid a spike in tensions between Russia and Japan following Russian President Vladimir Putin’s trip in August to the Kuril Islands, the Moscow-controlled Pacific archipelago that is claimed by both countries.

The Sakhalin region includes Sakhalin Island and the four southernmost islands of the Kuril chain, which Japan calls the Northern Territories.

Russia and Japan never signed a formal World War II peace treaty, with the main obstacle being the ⁠unresolved territorial dispute over the Kuril Islands.

Authorities in Russia have arrested numerous foreigners for alleged espionage since it invaded neighbouring Ukraine in 2022.

One of the most prominent cases was the detention of Wall Street Journal reporter Evan Gershkovich in 2023. He was found guilty of espionage by ‌a ‌Russian court, sentenced to 16 years and then freed in a major prisoner swap involving Russia and Western countries in August 2024.

Source link

Poland says two Turks arrested over Russia-linked Starlink station fire | Cybersecurity News

Warsaw says the 2 suspects held in Germany will face sabotage charges.

Two Turkish citizens have been detained in Germany over a fire at a Starlink station in central Poland that Warsaw has branded an act of sabotage carried out on Russia’s behalf.

Polish officials announced the arrests on Monday, one month after the fire, which they say was aimed at disrupting internet services, including for Ukraine’s military. The fire, in Masovia in Eastern Poland, engulfed the Starlink station’s power system and backup generator.

Recommended Stories

list of 2 itemsend of list

Polish Minister of Interior Marcin Kierwinski said the two men would face charges in Poland of carrying out sabotage on the instructions of a foreign intelligence agency. German police made the arrests on behalf of Polish services, according to Deutsche Welle. Polish officials did not say where or when in Germany the men were detained.

“We have no doubt that Russian services are behind this act of sabotage,” Special Services Minister Tomasz Siemoniak said in a news conference. “It is worth adding that Russian services are increasingly turning to individuals linked to the criminal underworld,” he said.

The case is the latest in a string of incidents that officials across the European Union deem to be part of a Russian campaign of sabotage and hybrid attacks aimed at eroding support for Ukraine.

The Russian embassy in Warsaw did not immediately reply to a request for comment. Moscow has previously dismissed similar accusations as baseless and the product of anti-Russian hysteria.

Ukraine’s military relies on tens of thousands of Starlink terminals for battlefield communications and occasional drone operations. Starlink founder Elon Musk activated the service over Ukraine in 2022, days after Russia’s full-scale invasion, following a plea from Kyiv. Poland has said it pays for Ukraine’s Starlink subscription.

Musk has since clashed with Ukrainian officials over his views on the war. This year, he also agreed to switch off thousands of Russian “grey-market” Starlink terminals in Ukraine, causing problems for Russian forces. Ukraine is now seeking to use the terminals for attacks on Russian territory.

Source link

UK police charge Royal Navy member accused of working with foreign power | Courts News

Police say the incident is not connected to ongoing investigations at the RAF Fairford airbase.

Police in the United Kingdom say they have arrested and charged a member of the Royal Navy accused of working with an unnamed foreign power after an investigation by counterterrorism police.

Teddy Young, 24, was charged with two offences under the National Security Act for allegedly obtaining protected information and preparing to transfer it for the benefit of a foreign power.

Recommended Stories

list of 4 itemsend of list

In a statement, authorities alleged that between November 2024 and May 2025, Young “obtained, copied, recorded or retained protected information, intending the conduct to benefit a foreign power… contrary to section 1 of the National Security Act 2023″.

Young is due to appear at London’s Westminster Magistrates’ Court later on Thursday.

“These are very serious charges against a serving member of the armed forces,” Commander Helen Flanagan, Head of Counter Terrorism Policing London, said in a statement.

“We have worked extremely closely with relevant operational colleagues within the Ministry of Defence as our investigation has progressed to ensure appropriate measures could be taken to mitigate any potential risks linked to this matter,” she added.

UK media reported that the officer was arrested at his home in Bedfordshire on Tuesday before he was taken into custody in London.

The police clarified that the case is not related to the ongoing investigation into an incident at the RAF Fairford airbase.

Source link

Former German spy chief arrested on suspicion of treason and espionage | Espionage News

August Hanning’s former chief of staff was also arrested on suspicion of ‘aiding and abetting attempted treason’.

Germany’s former foreign spy chief has been arrested on suspicion of espionage and treason, prosecutors have said.

August Hanning, 80, is under investigation for attempted treason and acting as an agent for a foreign intelligence service, the Office of the Federal Public Prosecutor General confirmed on Tuesday.

Hanning was president of Germany’s Federal Intelligence Service between 1998 and 2005.

He was arrested in Bad Toelz-Wolfratshausen in southern Germany. His former chief of staff, partially identified as Manfred D, was arrested in Steinfurt in western Germany on suspicion of “aiding and abetting attempted treason and treasonous espionage”.

The prosecutor’s office said, “On one occasion, Hanning used classified intelligence provided by Manfred D to draft an analysis for an officer of a foreign intelligence service.”

Prosecutors said Manfred D also served as the chief of staff for Hanning’s successors between 2012 and 2026, and used his role to gain access to confidential information which he then passed on to Hanning “in exchange for remuneration”. Hanning then used the information in his private consulting work, prosecutors added.

“The current findings suggest that, over the years, Manfred D provided Hanning with approximately 2,000 documents, many of which contained classified information to be used exclusively by the federal intelligence service for internal purposes, particularly for executive intelligence briefings,” the statement said.

The statement did not reveal who the two men were suspected of spying for or which country the foreign agent worked for, adding that “it has yet to be determined if the material reached the intended recipient”.

German MP Marc Henrichmann told the AFP news agency that Germany “will not tolerate the betrayal of secrets”.

Henrichmann, who chairs the German parliament’s intelligence oversight committee, said, “Whoever allies themselves with the enemies of our liberal democracy will be found out.”

The premises of Manfred D and Hanning were being searched in several locations, including in the capital, Berlin.

Source link

FBI arrests ‘Chinese foreign agent’ for spying on Taiwan president’s son | Espionage News

A California woman allegedly sent photos and videos of President Lai’s son and his family to Chinese officials.

The FBI has arrested a “Chinese foreign agent” at Los Angeles International Airport accused of spying on the Taiwanese president’s son.

Wanying Zhang, also known as Heather, was arrested on Sunday before her planned departure to China, the first assistant US attorney for the Central District of California, Bill Essayli, said in a post on X.

Recommended Stories

list of 3 itemsend of list

Authorities charged Zhang, 34, of Irvine, California, with acting as an unregistered foreign agent.

Zhang surveilled Taiwanese President William Lai Ching-te’s son, the FBI said. The agency did not directly name Zhang’s alleged target, but later shared a news article identifying him as Lai Ting-yu.

The US Justice Department said Zhang travelled to Seattle in 2025 at the behest of Chinese officials. She sent photos, video and license plate information of the Taiwanese leader’s son and his family to China.

Essayli called Zhang a “Chinese foreign agent” and said she “used tradecraft to avoid detection”.

“She never notified the Attorney General she was acting for a foreign government, a federal offense,” he added.

Essayli said Zhang will appear in a Los Angeles federal court on Monday.

William Lai Ching-te and his Democratic Progressive Party say that Taiwan is already an independent country separate from China. Beijing views the island as Chinese territory.

Washington does not have ⁠formal diplomatic ties with Taiwan, but the US is bound by law to provide the island with the means to ‌defend itself.

Earlier this week, the US delivered two F-16V ⁠Block 70 fighter jets to Taiwan as the island seeks to build its defence capabilities to deter a feared attack by China.

In January, Chinese President Xi Jinping pledged to achieve the “reunification” of China and Taiwan, calling Beijing’s long-held goal “unstoppable”.

Source link