Hackers have twice taken control of supermarket fridges across Europe in less than a month, sparking fires and spoiling millions of euros’ worth of food.
On October 11 and 12, attackers heated units at about 700 French stores to as high as 50C (122F). On November 2, a second wave of suspected cyberattacks affected supermarkets and food businesses in at least nine European countries, including Belgium, Estonia, Finland, Ireland, Italy, Luxembourg, the Netherlands, Portugal and Sweden.
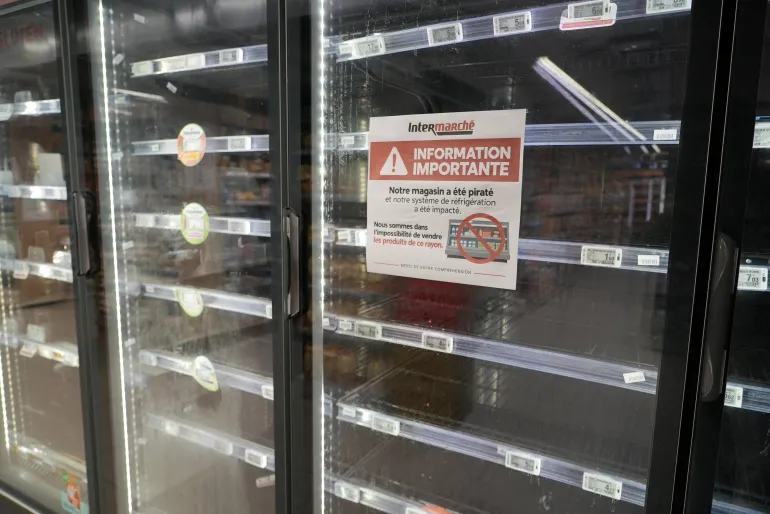
Empty freezers at a Paris supermarket after the October 2026 cyberattack on French stores’ refrigeration systems. The sign reads: ‘Our store has been hacked, and our refrigeration system has been affected.’ [Lucien Libert/Reuters]
France has since blamed the first attack on Shahid Kaveh, a cyberunit affiliated with Iran’s Islamic Revolutionary Guard Corps (IRGC), calling it the first large-scale sabotage cyberattack on French soil. It is not yet clear who was behind the second wave.
The attacks have raised concern about how exposed internet-connected equipment has become, from industrial machinery to household appliances. Al Jazeera illustrates the devices at risk in your home and the essential services you rely on, and what you can do to protect yourself.
How can a fridge be hacked?
A supermarket’s fridges and freezers are run from one control panel, which is connected to the internet so contractors can manage it remotely. Home smart fridges connect the same way, through Wi-Fi, an app or a cloud service.
The attackers reportedly found the supermarket systems using Shodan, a search engine for internet-connected devices. According to Vincent Strubel, head of France’s National Cybersecurity Agency (ANSSI), they got in through basic security failures:
Exposed: The equipment was directly connected to the open internet with no extra protection.
Weak passwords: Many systems were protected only by weak or default logins.
Outdated: Many units were old models that no longer get security updates.
Once inside, hackers can switch a fridge off, raise its temperature or steal account details. In France, they simply used the controllers’ own defrost function. A poorly protected fridge can also be a doorway to other devices on the same network, from laptops to smart locks.
Speaking to the French Senate on October 21, Strubel warned that the healthcare sector uses the same type of equipment to store vaccines and hazardous materials, from research laboratories to pharmacies.
How hackable is your home?
Essentially, anything connected via the internet could potentially be hacked.
There are about 21 billion short-range connected devices, such as smartwatches, worldwide and 5.4 billion long-range ones, such as remote monitoring systems, according to Kepios’s Digital 2027 Global Overview Report. US internet households now have an average of about 18 connected devices, nearly double the number a decade ago, according to Parks Associates.
Routers are among the biggest targets because they are always online. In April, the UK’s National Cyber Security Centre (NCSC) warned that hackers linked to Russia’s GRU military intelligence were hijacking home and small business routers. By tampering with their DNS settings, which turn website names into IP addresses, the hackers redirected users to fake websites to steal passwords and personal details.
Smart TVs can be hacked without their owners knowing. In June, researchers found that more than a third of apps on LG and Samsung smart TVs could let strangers secretly use a household’s internet connection, hiding their own activity behind that home’s IP address.
Robot vacuums can expose even more. Earlier this year, a programmer reportedly found he could control almost 7,000 DJI Romo robot vacuums with a PlayStation 5 controller. Using Claude Code, an AI coding tool made by Anthropic, to work out how the vacuums talked to DJI’s servers, he gained access to their live camera feeds, audio and floor plans of people’s homes.
What vital services can be hacked?
The same weaknesses that expose a fridge can affect power plants, water supplies, banks and hospitals.
Many of these services are run by industrial computers that can be reached online. Since the US-Israel war on Iran began, US agencies have warned that Iran-affiliated hackers are attacking these systems.
In July, a cyberattack in the US state of Minnesota targeted more than 30 community water systems, according to the state’s IT agency. Officials suspected Iran-aligned hackers, and the FBI and CISA warned that water and wastewater systems were increasingly being targeted, with facilities in 12 states affected at the time.
That same month, a cyberattack attributed to Iran-linked hackers forced a small British power plant offline for four days. It was reported as the first successful attack of its kind on UK energy infrastructure.
The US Cybersecurity and Infrastructure Security Agency (CISA) lists sectors it considers critical infrastructure. The graphic below shows some of the key ones, and what a hack on each could mean for you.
Banks are targets, too. In late September and early October, hackers stole personal data from at least seven South Korean financial firms, affecting about 68,000 people. Yegaram Savings Bank and Shinhan Bank were hit hardest, with about 40,000 and 25,000 customers affected, respectively.
According to The Wall Street Journal, the attacker used ARTEX, an open-source AI tool developed in China to test networks for weaknesses. US cybersecurity firm CrowdStrike said the attacker was likely a China-based individual who also used Claude Code, an assessment it made with moderate confidence.
Which industries are most politically targeted?
The European Repository of Cyber Incidents (EuRepoC), a research database tracking political cyberattacks worldwide, logged 4,932 major incidents between January 2000 and November 2026.
The number of incidents has grown sharply in recent years, peaking at 795 in 2024. About two-thirds of all incidents recorded since 2000 have occurred since 2022.
Governments are the biggest target. State institutions account for nearly 40 percent of all targets, led by the civil service and government ministries, followed by the military, police, political parties and legislatures.
Critical infrastructure is the second most targeted sector, led by health, finance, telecommunications, transport and energy, followed by defence firms, manufacturing, research and digital service providers. Companies, schools, civil society groups and media outlets make up most of the rest.
EuRepoC tracks only politically significant attacks, a fraction of all cyberattacks. Beyond these, hackers often target individuals and companies with scams.
How to protect oneself?
Hackers rely on weaknesses such as weak passwords and devices that no longer receive updates.
Awais Rashid, a professor of cybersecurity at the University of Bristol, told Al Jazeera that as infrastructure becomes more digitised, the risk of disruption from cyberattacks has risen. But, he added, “the world works because cybersecurity works effectively”.
The UK’s NCSC also advises people to turn off features they don’t use, such as remote camera access.
If a power plant or water system is hacked, there is little individuals can do. The UK’s Be Ready campaign, launched last month partly in response to cyber-threats, urges households to keep a three-day supply of water, food, medicine, cash and torches.
The graphic below shows five simple steps you can take to protect yourself from hackers.
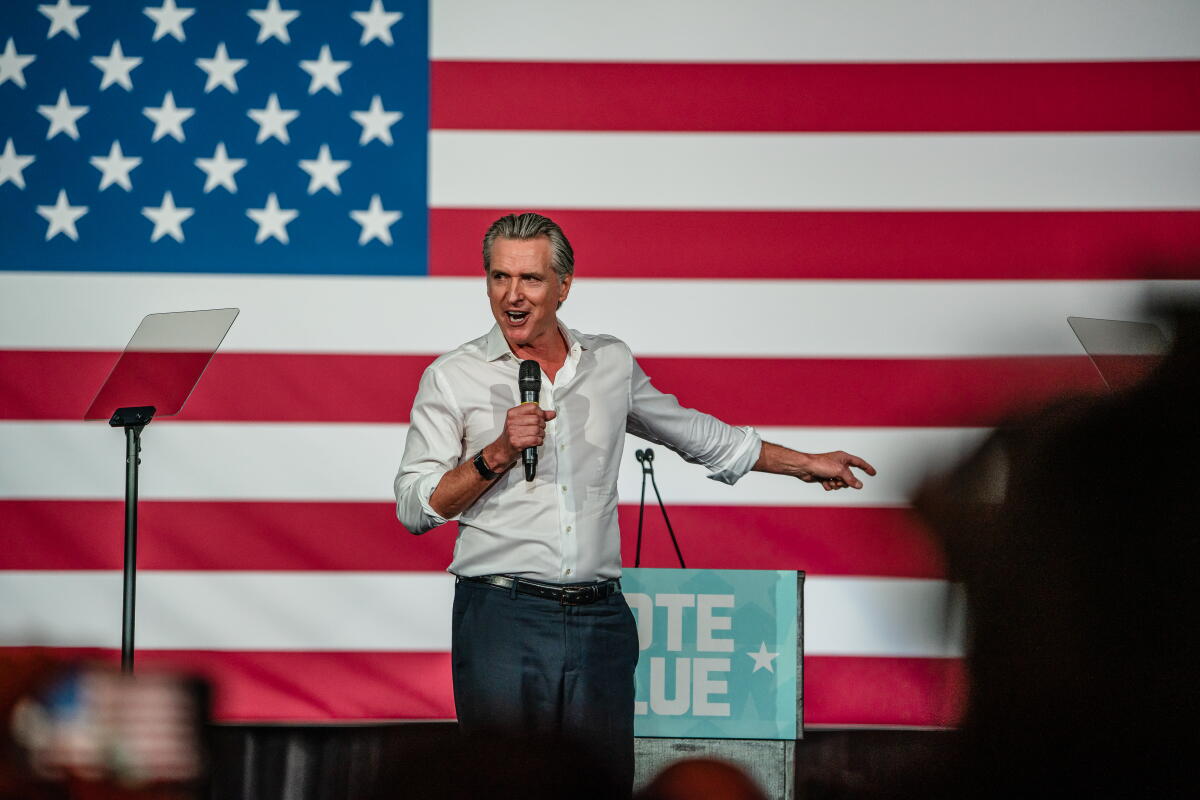
Amid a hum of speculation about how the mass commutation could help or hurt his presidential prospects in 2028, the Democratic politician sent a clear, defining message to Americans about where he stands and the type of leader they could expect.
“If my job is just to read the polls, you can have an AI chatbot as governor,” Newsom said in an interview Friday. “I was hired for my judgment, and like it or hate it, that was why I think I was given this privilege, and that’s the responsibility of a leader. My job’s leadership, not stewardship. It’s not management. It’s to lead.
The Democratic governor said those kinds of decisions are “sort of embedded in my DNA.” About a decade ago he said he was pushed to describe his core motivation. Though he admits it sounds trite, the governor said: “It’s to stand up for ideals and strike out against injustice.”
The death penalty, he said, is not handed out equally. He quoted Bryan Stevenson, the founder of Equal Justice Initiative, who said you’re better off being rich and guilty than poor and innocent.
“I couldn’t not have done this,” Newsom said. “There was an easy out, but … I would the rest of my life felt, you know, ashamed of myself.”
Commuting the death sentences of all 548 state prisoners awaiting execution pushes the bounds of his authority once again. California voters have twice rejected ballot measures to abolish the death penalty, first in 2012 and again in 2016, and Newsom’s decision overrides the will of the courts and state laws that permit capital punishment.
Under the state Constitution, Newsom has the power to commute about 40% of the death sentences on his own. The rest of the cases, which involve prisoners who had a felony conviction on their record prior to receiving a death sentence, or racked up additional crimes while awaiting execution, require approval from the California Supreme Court — a constitutional check to ensure the governor’s actions are not an abuse of power.
The court rejected 10 commutations handed out by Gov. Jerry Brown in his last full month in office — all of which involved people convicted of multiple felonies — and did not provide an explanation for the action.
Despite Newsom’s push to commute all death sentences, capital punishment remains legal in California and prosecutors can continue seeking that punishment.
Los Angeles County Dist. Atty. Nathan Hochman speaks during a news conference at the Hall of Justice last month.
(Ronaldo Bolaños / Los Angeles Times)
Los Angeles County Dist. Atty. Nathan Hochman said until the law is changed, his office “will continue to evaluate every death penalty-eligible case with the rigor, care and restraint these decisions demand.”
Sacramento County Sheriff Jim Cooper urged Newsom to reconsider the commutations.
“Deputy Danny Oliver and Detective Michael Davis Jr. should be alive today, enjoying long and healthy lives with their families,” Cooper said in a statement. “Instead, the man who murdered them has now escaped his sentence.”
Others accused the governor of reducing the death penalty sentences to seek an advantage in the 2028 presidential election.
“The people of California deserve leaders who put politics and personal ambition aside and pursue truth, accountability, and justice with courage, integrity, and transparency,” said Michael Hestrin, Riverside County district attorney, in a statement. “Instead they have been presented with a decision that demonstrates a profound disregard for the victims, their families, and the prosecutors who dedicated themselves to seeking justice on their behalf.”
Luis Bracamontes looks up in Sacramento Superior Court in 2018 as the verdict is read in the killing of two law enforcement officers. Bracamontes was found guilty.
(Rich Pedroncelli / Associated Press)
A poll conducted in August by the Pew Research Center found that about two-thirds of voters nationally favor the death penalty for people convicted of murder.
Political analysts suggest that reducing the sentences adds to Newsom’s credentials as a progressive leader and aligns him with Democratic primary voters on the issue if he runs for president. Republicans, however, could take advantage of Newsom’s action and cast him as a soft-on-crime liberal who is out of touch with most Americans, which risks turning away moderate voters.
But others cautioned that national political elections are hard to predict.
Gar Culbert, chair of the political science department at Cal State Los Angeles, said it would be politically advantageous for Newsom to try to appeal to the Democratic Party’s base as he considers a run for president. Culbert said he doesn’t believe the death penalty will be a substantial issue in a general election when, if Newsom becomes the Democratic presidential nominee, his Republican challenger would attack his record as California governor regardless.
“It’s possible he’s not being strategic,” Culbert said. “Maybe he doesn’t have to be strategic because he just might think it’s the right thing to do.”
The governor first issued a moratorium on executions about two months after he took office in 2019, saying capital punishment is discriminatory and unjust. Without the moratorium, 45 people would be subject to execution now, according to his office.
Daniel Zingale worked for Newsom as a senior advisor in the governor’s office at the start of his first term. Part of Zingale’s job at the time was to consider how the governor’s actions would be received by the public.
“The only piece of data he was not interested in in that process were the polls,” Zingale said. “His view, and I agree with this, is this is not an issue that you can leverage politically.”
Newsom’s decision to commute the sentences won’t have much practical effect in a state that has not executed a prisoner since 2006. At Newsom’s command, the death chamber was dismantled at San Quentin State Prison, now San Quentin Rehabilitation Center, after he issued his moratorium.
His successor, Gov.-elect Xavier Becerra, has also said he will continue the pause on executions.
There was no immediate need to offer commutations to save the lives of the inmates.
Taking no action would have been the safe bet, Newsom said in an interview about his decision a day after he made the announcement. Many people around him, he said, advised him to do nothing.
He also understands that commuting the sentences could make him vulnerable if he runs for president.
“I’m not an idiot. The ads write themselves,” Newsom said. “But I just also would be fake. I wouldn’t be myself and if I’m going to be up there and not be myself, I couldn’t do that.”
With the clock ticking on his time in office, the governor said he also doesn’t want to leave with regrets.
“I don’t want to be one of the elders on some panel talking about what I would have, could have, should have done,” Newsom said. “I’ve spent my life trying not to be that person. I’ve been willing to take risks. I’ve been willing to go first on so many issues.
“If others aren’t willing to do it, you know what? I’ll raise my hand, and I’m happy, honestly, to take the hits.”
A new report from the think tank founded by former Google CEO Eric Schmidt quantifies the grim realities of the U.S. defense industrial base’s dependence on China for critical rare earth minerals. It also details which weapons systems might face the most impact if that delicate supply relationship breaks down.
The white paper, exclusively obtained from the Special Competitive Studies Project, uses AI intelligence from the supply chain tech firm Exiger to assess how many unique components, identified by National Item Identification Number, or NIIN, contain critical minerals, such as antimony, gallium, germanium and tungsten.
America’s arsenal depends on a steady flow of rare earths, and especially its most advanced weapons. U.S. Air Force photo by Tech Sgt. Thomas Barley Tech. Sgt. Thomas Barley
From an assessment of almost nine million parts and 3,000 U.S. military weapon systems, the company identified more than 28,000 unique components across 1,400 weapons systems containing just these four rare earths. The isolation of these parts is relevant in particular because of a near-term crisis: the expiration of a suspension on Chinese export controls set to take effect in November. Disruption to weapons fielding plans, as well as operational readiness and sustainment activities, according to the white paper, is very much a possibility. Yet according to Kit Conklin, chief strategy and global affairs officer at Exiger, the crisis is already here.
“There’s no question that right now it’s a crisis for a lot of companies that are trying to get licenses approved by China and just not getting the licenses,” Conklin said. “So there’s real risk to current production, and when I think about us and scaling, whether it’s the drone industrial base or trying to scale our interceptor capacity to 1,000, 2,000, 3,000 interceptors a year, I mean, these are real choke points that we have that are impacting our ability to deliver these to the warfighter right now.”
Among the weapons systems most at risk for supply chain and manufacturing disruption, according to the data, is the vital Virginia-class submarine, which requires more than 300 critical NIINs containing the four elements, including 190 parts requiring germanium.
USS Virginia (SSN 774), the leader of the Virginia class that serves as the backbone of the U.S. Navy’s fast attack submarine force. U.S. Navy photo by General Dynamics Electric Boat U.S. Navy
Germanium, used in optics, night vision systems, EO/IR equipment and more, is a byproduct of zinc ore. In January, the Pentagon announced an $18 million investment in the country’s only germanium production facility in St. George, Utah to expand refining capacity “sevenfold” to more than 20 metric tons annually by an unspecified deadline.
China controls some 68% of the world’s refined germanium. It has a far greater chokehold on gallium, used in semiconductors and solar cells, and especially advanced radars, controlling up to 99% of production. Each Virginia-class sub requires 50 unique parts containing gallium.
China controls about half the production of antimony, used to harden ammunition and to manufacture optics and electronics; and up to 80% of the supply of tungsten, used in manufacturing tools, warheads and heat-resistant components.
While it doesn’t break down components by weight, the report notes that the rare earth requirements for the Virginia-class sub are also considerable by mass: each sub required 9,200 pounds of the elements, while an F-35 Joint Strike Fighter jet requires 900 pounds.
Special Competitive Studies Project
The Virginia-class submarine is America’s only in-production fast-attack nuclear-powered sub that has been in service since 2004. Twenty three of these critical vessels are in service today, or roughly half of the total planned program, with the remaining boats yet to be built. It’s notable in the context of the paper because it has multiple points of exposure to supply chain disruption. Another of these exposure points: its 1,700 mission or safety-critical parts requiring casting, forging or extrusion. As the report lays out, supply chain bottlenecks around limited metal casting, forging and extruding capacity are delaying production timelines and putting manufacturing at risk.
China, again, produces about half of the world’s casting output and “is often the sole option for large castings,” the paper found. The analysis shows that more than half, or nearly 8,000, unique supply items containing steel castings have delivery lead times of more than 36 weeks. More than 9,400 items containing extruded aluminum, about 47% of these parts, have lead times that long.
A large metal casting for a port crane. Voestalpine Foundry Group
“Virginia-class submarines, already threatened by U.S. reliance on China for critical minerals, are reportedly also three years behind schedule, potentially due in part to the lack of domestic large-scale casting capacity,” the report finds. An analysis of Navy construction timelines published earlier this year does indeed find that 10 of the 12 Virginia subs now under construction face delays of 36-44 months.
Alarmingly, a recent war game simulation found that the U.S. could not replace ships, planes and missiles lost to combat specifically due to casting and forging shortfalls, the report notes. That’s despite a $2 billion Pentagon initiative launched in 2024 aimed at revitalizing this industry.
Beyond submarines, the report shows that aircraft, including some of the nation’s workhorse fighter jets, face outsized production and sustainment risk due to rare-earth elements and casting/forging dependencies.
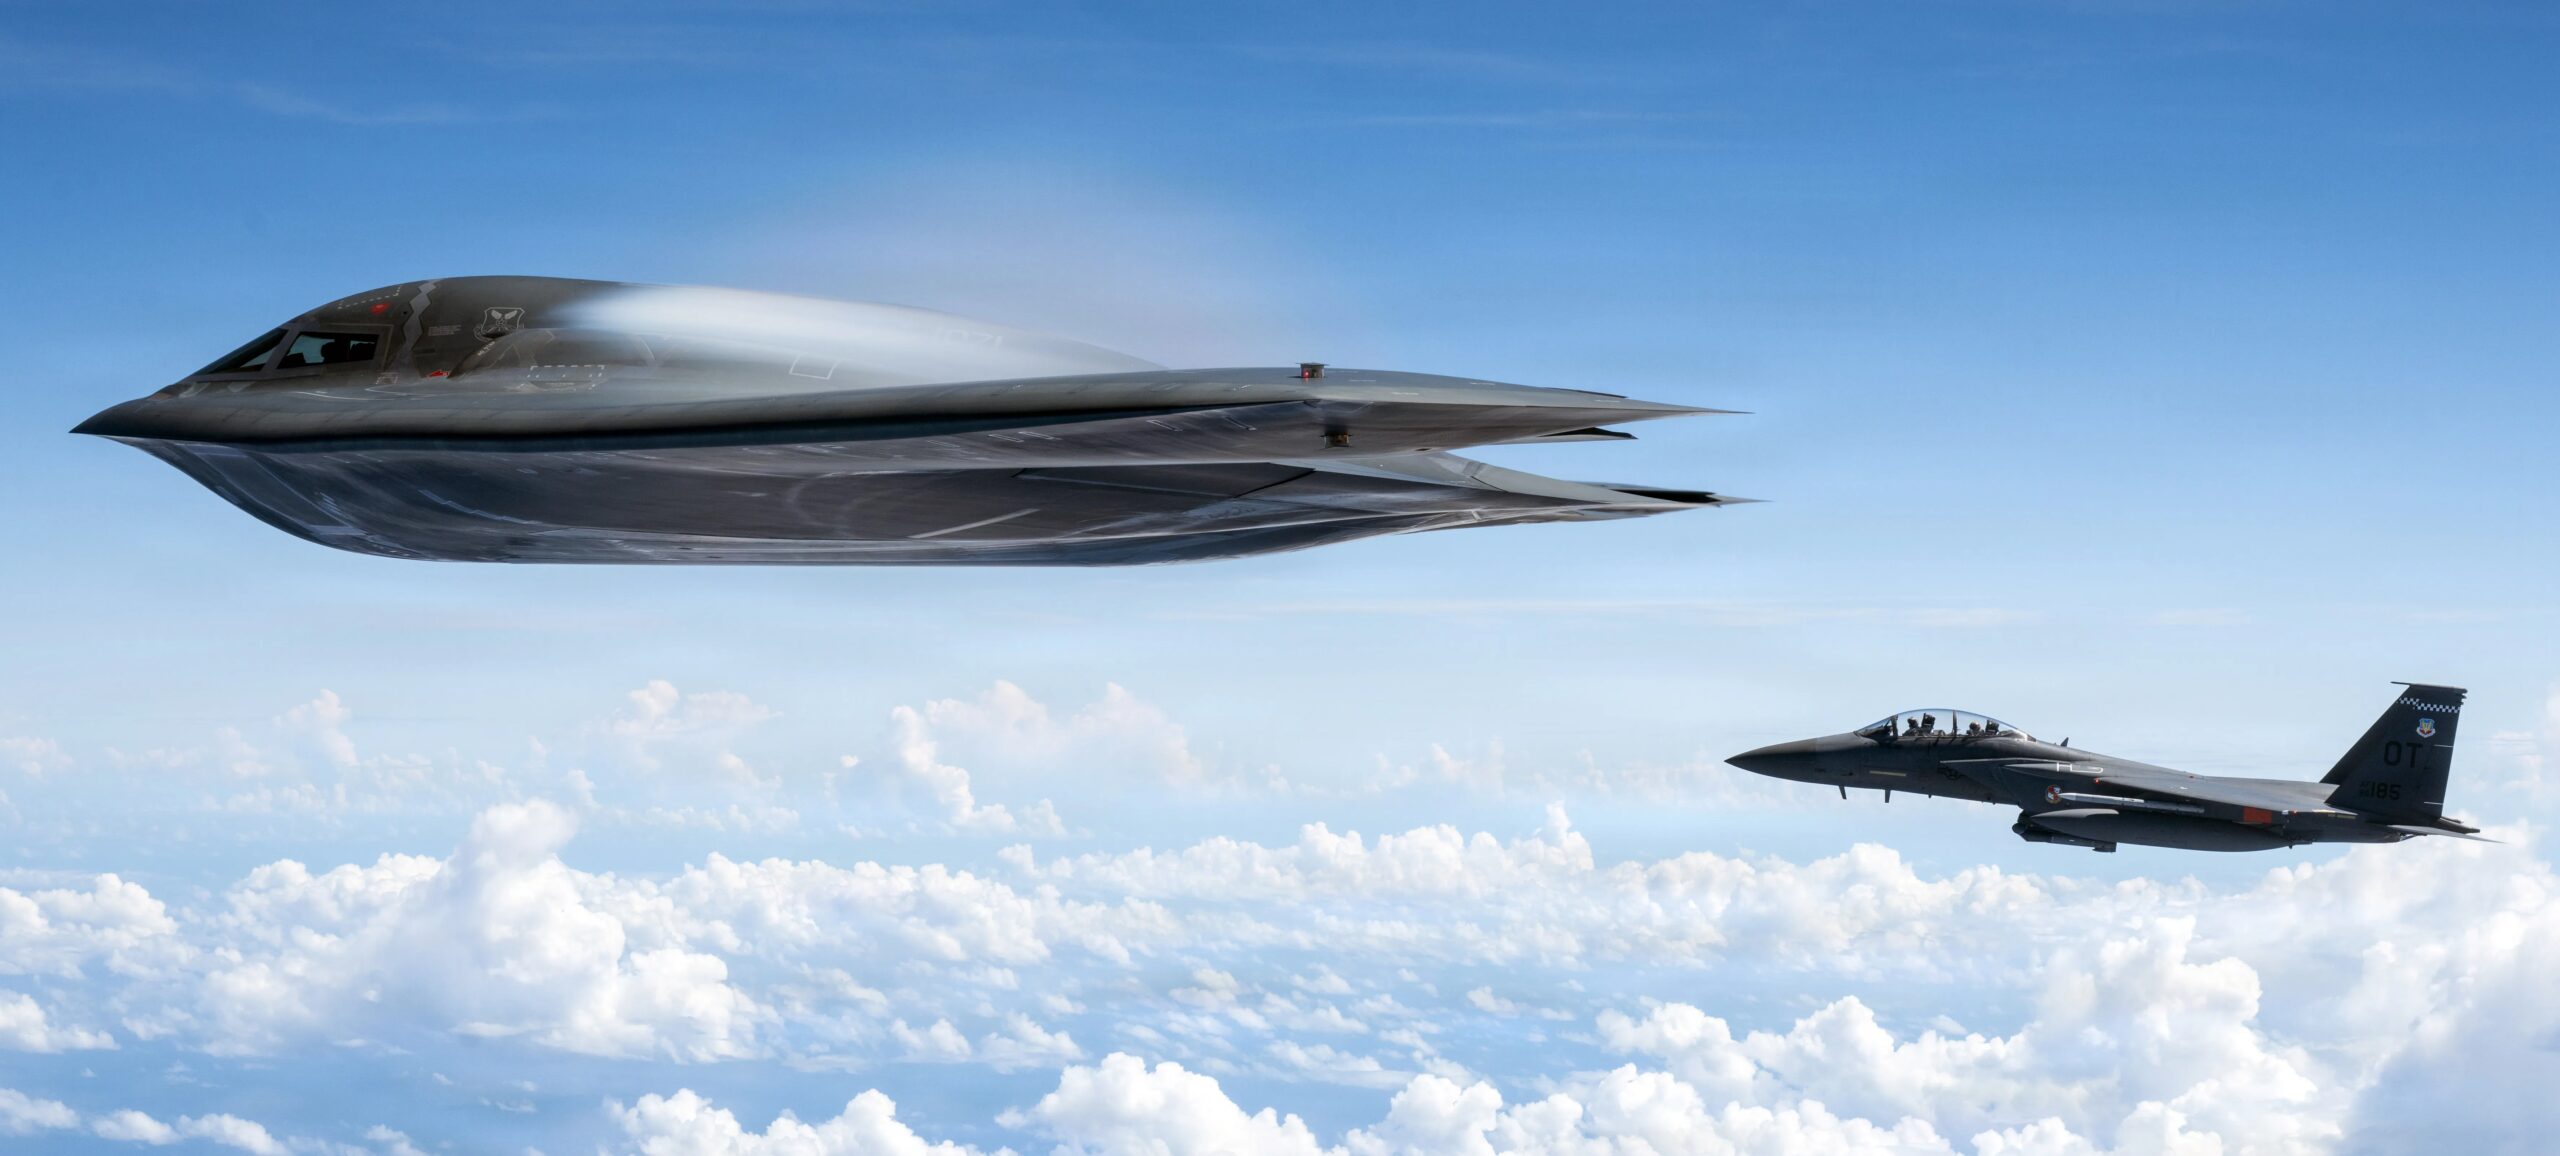
The B-2 Spirit bomber – the nation’s only nuclear-armed stealth bomber until fielding begins on the B-21 Raider sometime next year – requires 782 parts containing the four rare-earth elements isolated in the report.
Special Competitive Studies Project
The F/A-18 Hornet family of fighters flown by the Navy and Marine Corps, including the Navy’s Growler electronic warfare variant, tops the list for dependency on steel castings, with 3,800 individual parts requiring the process. Following is the KC-135 Stratotanker, with 2,570 parts. All 10 of the systems requiring the most metal castings for production are aircraft, the analysis shows. The legacy Hornet and the KC-135 have been out of production for decades, while the Navy’s Super Hornet will see its production line go cold in 2027. Any ongoing demand for castings for these systems would thus be in spares and repair parts.
Special Competitive Studies Project
Military aircraft also represent the highest-need category among weapons systems requiring cadmium plating, a process used to make aerospace components corrosion-resistant. The domestic supplier base has shrunk due to EPA safety limitations established in 2008. All of the top 10 weapons systems requiring the most cadmium-plated parts are aircraft, with the KC-135 topping the list with 2,780 unique components. The C-130 Hercules transport, B-52 Stratofortress bomber and Galaxy C-5 transport all have more than 2,000 parts.
Special Competitive Studies Project
The B-52, which is undergoing a service life extension to take it into the 2050s – past its century mark – may run into modernization delays not only over cadmium-plated and steel-casted components, but also due to overly rigid military specifications, which increase lead time and delays. The white paper cites the bomber’s rib airfoil and fuel vent valve components, which both have lead times of more than 400 days due in part to production being burdened with dozens of mil-spec compliance requirements, which the authors say have not kept pace with today’s commercial practices.
“The requirement for a part to meet so many mil-specs, if not reasonably necessary, may limit the number of possible suppliers of that part, potentially increasing its lead time and bottlenecking production,” they write. “For the B-52, this could inhibit current modernization efforts intended to keep the airplane operational through the 2050s.”
A B-52H Stratofortress undergoing programmed depot maintenance is towed into a hangar at Tinker Air Force Base, Oklahoma, July 28, 2025. U.S. Air Force photo by Paul Shirk Paul Shirk
A final risk the paper addresses is workforce shortages and dangers from limited suppliers creating single points of failure. Across defense, the number of small suppliers has decreased by 43% in the last decade, it notes. It cites, as a case study, the February 2025 fire that forced the closure of SPS Technologies in Jenkintown, Penn. – a fastener maker that produced components for more than 1,000 weapons systems and was deemed critical for 90, including the Nimitz-class carrier, the F/A-18 fighter and the M1 Abrams tank. For systems including the Tomahawk Land Attack Missile and the MH-60 Black Hawk helicopter, the facility was a single-source supplier.
With operations offline until at least 2028, the supply chain has been “actively disrupted” due to the outage of just one facility, according to the paper.
“This case underscores the risk of single sourcing in the defense industrial base and the need to qualify alternate sources to avoid such significant chokepoints,” the authors write.
The paper hails work that has already begun to invest in domestic critical minerals production and shore up the defense industrial base. But it does hint that these efforts may be too late to avoid a crash if China shuts off or severely reduces exports. The paper notes that, on average, it takes the U.S. 29 years to open a new mine. The U.S. has one established domestic mine: The Mountain Pass Rare Earth Mine and Processing Facility, just outside of Las Vegas. Initially established in 1952 and reopened in 2018 after a long hiatus, it now produces more than 50,000 tons of rare earth oxides annually. Last year, for the first time in seven decades, a new domestic rare-earth mine opened in Wyoming, stating plans to start producing ores extracted from coal, including gallium and germanium, by 2029. Production is projected to total 456 tons of rare earths per year. The project had been in development for more than a decade before opening.
The Mountain Pass Rare Earth Mine and Processing Facility. MP Materials
Conklin said a July executive order aimed at developing domestic production of rare earths while collecting data on what elements systems required created opportunities for smart policy creation – perhaps in the next National Defense Authorization Act – around holistically attacking the problem.
“I would love for us to figure out a way to get out of thinking about these supply chain risks system by system. We tend to have disparate requirements to look at the nuclear triad or subs or interceptors,” he said. “I think with the executive order that came out earlier this year, there’s a real opportunity for Congress to legislate on some of these issues beyond just figuring out what the risk [is] for antimony in the sub industrial base, and thinking about it a little bit more holistically.”
One potential solution he proposed: an agency within the executive branch (led, perhaps, by a critical minerals czar) who can coordinate production needs and resourcing and develop the most efficient pathways to secure needed materials.
There are few weapons that are not impacted by the scarcity of robust sources for rare earths. RTX
While no U.S. defense manufacturer has yet publicly cited manufacturing disruptions due to rare earth availability, signs are increasing that the federal government is taking supply concerns seriously. In addition to Project Vault, a $12 billion White House initiative announced in February that would create a strategic stockpile of rare earths akin to existing stockpiles of critical medical supplies and petroleum, the U.S. Army has begun extending long-term leases on military land to companies seeking to build critical mineral processing facilities.
Conklin said he doesn’t anticipate major changes in rare earth exports between now and the end of the year, describing the U.S.-China supply relationship as “in a bit of a détente.” That said, with new policies pending, we could be only days away from new revelations about the extent of the impact of these materials on the defense manufacturing enterprise.
A UK travel company that sells holidays to Turkey, Greece and Portugal has entered administration after nearly four decades.
Wroxham Travel first opened in 1987 as an independent travel agency selling holidays to numerous destinations including UK staycations, short-haul trips and long-haul holidays.
Wroxham Travel has entered administration after 39 yearsCredit: Alamy
The company also sold ocean and river cruise trips.
However, the Norwich-based company officially closed on October 30.
Sign up for the Travel newsletter
Thank you!
The company had two high street stores – one in Hoveton and one in Aylsham.
While the impact of the company’s closure isn’t clear, it is expected to primarily affect holidaymakers in the Norfolk and Greater Norwich areas.
The Association of British Travel Agents (ABTA) said in a statement: “We are sorry to inform you that Wroxham Travel has ceased trading with effect from 30 October 2026.
“We are now treating this as a financial failure.
The company used to sell holidays to the likes of Turkey and GreeceCredit: Alamy
“If you booked a holiday through Wroxham Travel, the tour operator or principal business with whom Wroxham Travel booked your holiday will be named on your paperwork (or ATOL certificate if it was a flight inclusive holiday; this would be stated on your ATOL certificate under “Who is protecting your trip”).
“To ensure your holiday can continue as planned, you will need to contact the credit control department of your tour operator or other principal travel business with whom you have a contract.
“Your booking should continue as normal, and they will be your direct point of contact.
“Please ensure that you have all your documentation with you, as they may require information from it to assist you.”
Authorities vow firm action against violence as yellow vest and student movements announce widespread demonstrations.
Published On 29 Oct 202629 Oct 2026
France’s interior minister has announced the deployment of 70,000 police officers across the country in preparation for planned protests on Saturday, coinciding with Halloween.
Interior Minister Laurent Nunez said on Thursday that security measures, including the use of armoured vehicles and water cannon introduced last week, will be strengthened.
Recommended Stories
list of 4 itemsend of list
Nationwide protests over the rising cost of living have rocked France, with some degenerating into large-scale looting and riots.
“The day of October 31 presents a very high risk of public disorder,” Nunez said at a news conference.
About 70,000 police officers and gendarmes will be mobilised, matching the number deployed at last week’s protests, he said, calling the move an “exceptional measure”.
Demonstrations last Saturday drew about 410,000 protesters nationwide, according to the interior ministry, though unions put the figure at roughly double that. The ministry said more than 2,700 people were arrested a week earlier.
A protester taking cover behind a sheet of particleboard throws a rock at riot police during a protest in Paris on October 24, 2026 [Manu Brabo/Getty Images]
Warning on Halloween masking
The “yellow vest” movement and student unions have called for a new day of protests on Saturday.
Nunez warned demonstrators against using Halloween as “a legitimate reason to hide one’s face” to cause disturbances in public areas.
He told reporters demonstrations would be allowed, but “not in city centres, where there is a risk of public disorder”.
The interior minister issued a warning to far-right groups that clashed with left-wing protesters at rallies in about 15 French cities.
“We will tolerate no excesses,” he said, and pledged an “extremely firm” response.
Nunez accused the “ultra-left” movement and some yellow vest activists of circulating messages on social media promoting demonstrations on Halloween evening that called for a “revolution”.
“These gatherings will be banned,” he said.
The yellow vest movement has already announced a “third act” of its protests on Halloween and called for demonstrations outside the National Assembly and all town halls in the country.
The world authority on threatened wildlife classified 96 percent of all coral reef systems as “critically endangered”.
By AFP and The Associated Press
Published On 22 Oct 202622 Oct 2026
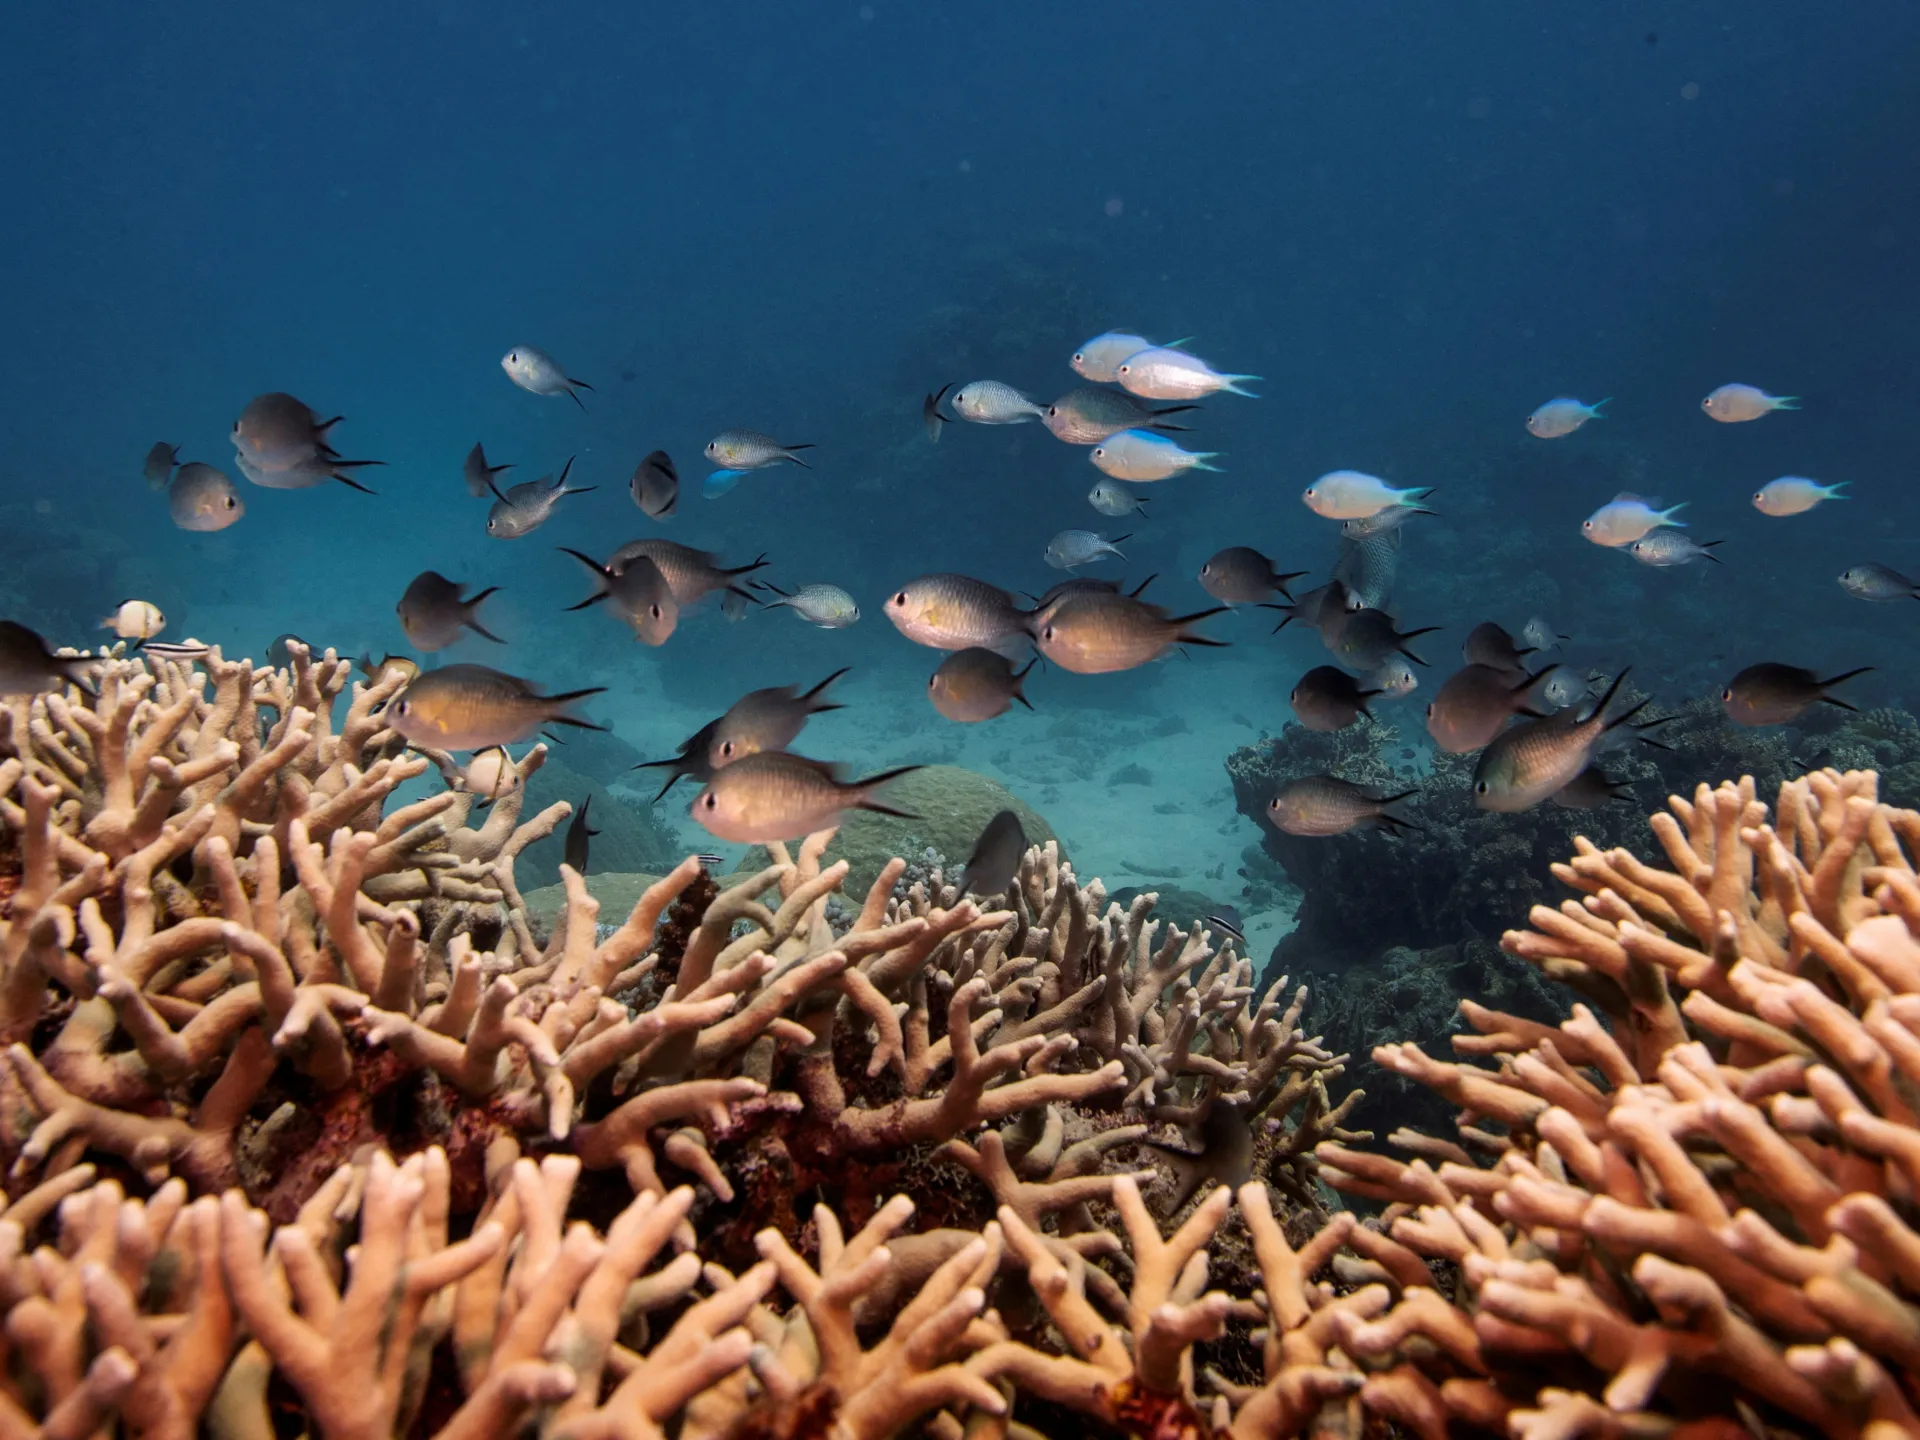
Almost all of the world’s shallow-water coral reefs face an extremely high risk of collapse in the next 50 years, the International Union for Conservation of Nature (IUCN) has warned in a new global assessment.
In a report released on Thursday, the world authority on threatened wildlife classified 96 percent of the planet’s coral reef systems as “critically endangered”, its highest risk category, with total extinction possible by 2075.
Recommended Stories
list of 4 itemsend of list
“The future threat of climate change is looming and severe, and that poses a very high risk to the survival of these ecosystems,” said Mishal Gudka, scientific lead of the IUCN Red List of Coral Reef Ecosystems assessment.
Corals are heat-sensitive and particularly vulnerable to human-driven climate change, which is warming the world’s oceans and increasing the frequency and intensity of damaging bleaching events.
When a reef collapses, hard corals disappear and are replaced by algae, rubble and sponges. As a result, the reef no longer supports a diverse ecosystem that can include everything from tiny invertebrates to reef fish like grouper.
The emergence this year of a “super” El Nino, the natural warming phenomenon, also presents a risk to corals, Gudka said at a news conference at the UN’s COP17 biodiversity summit in Yerevan, Armenia.
It’s the latest dose of bad news for coral reefs, which are critical sources for seafood and tourism and often serve as buffers against coastal erosion and storms.
Sometimes dubbed “rainforests of the sea”, they have some of the world’s richest biodiversity and support a quarter of marine species as well as coastal communities and businesses.
Most of the world’s famous reef systems – including the Great Barrier Reef in Australia, the Coral Triangle in the Western Pacific Ocean and Southeast Asia, the Mesoamerican Barrier Reef System and the Red Sea coral reefs – are critically endangered, according to the assessment.
Elevated risk of extinction
For its report, the IUCN used the “middle-of-the-road” scenario from the UN’s panel of climate experts that projects global temperatures rising 2.7C above pre-industrial levels by 2100.
Its analysis examined 127 tropical and subtropical coral systems covering 188,362 square kilometres.
A week ago, another IUCN study in the journal Nature found that nearly 44 percent of reef-building coral species face an elevated risk of extinction due to climate change. A year ago, a survey found that harmful bleaching of the world’s coral had grown to include 84 percent of the ocean’s reefs, the most intense of its kind in recorded history.
Despite its warning, the IUCN said coral reefs in most parts of the world “are not yet lost”.
“Coral reefs have shown a remarkable ability to bounce back from devastating bleaching events,” said Gudka. “Pockets of surviving, resilient coral reefs can still remain in the future, so we must do everything within our reach to set them up for success.”
The Celebrity Traitors is back on BBC One tonight with a murder in plain sight taking place – but a Traitor, namely Love Island’s Maya Jama, could be in the frame too, it has been claimed.
Maya Jama has a ‘tell’ at the round table says a body language expert
Until now, the virus was considered non-transferable to humans, making the patient the first documented human case.
Published On 22 Oct 202622 Oct 2026
French authorities have confirmed that a patient who died at a Lyon hospital earlier in October was infected with the Shamonda virus, the first such report of the virus in a human.
In a statement on Thursday, the French Ministry of Agriculture stressed that there were no identifiable health risks to the general population at this time.
Recommended Stories
list of 4 itemsend of list
Shamonda is an orthobunyavirus – a group of viruses primarily carried and spread by insects – transmitted to animals, mainly cattle, by biting midges of the genus Culicoides.
It was first detected in Nigeria in the 1960s, but has since been reported sporadically in East and Southern Africa, as well as Japan.
Until now, the virus was considered non-transmissible to humans, making the patient in France the first documented human case.
The French announcement said the leading hypothesis was that the patient was infected in eastern France, where the virus had circulated among animals this spring and summer.
“Clinical, biological and epidemiological investigations are continuing in conjunction with expertise in human, animal and environmental health,” the statement added.
Shamonda was first confirmed in Europe in late July after genomic tests on sick cattle in southern Germany, Switzerland and eastern France.
A report from France’s weekly animal health surveillance bulletin said the virus had also been detected in Austria, Belgium, Ireland, Italy, Liechtenstein, Luxembourg, the Netherlands, Portugal, Slovenia, Spain, and the United Kingdom’s Jersey.
Just visiting a page or refreshing an app can be enough to fall victim to a malware attack in which your personal data is stolen from a laptop or phone, researchers have found. You are not even required to “click” on anything.
An Israeli spyware firm has been found to be behind the first-known instance of “zero-click” targeted advertising in which fraudsters or spies can steal private data and send it to external servers, with Al Jazeera journalists among the victims.
Recommended Stories
list of 3 itemsend of list
In June 2025, 45 devices used by Al Jazeera staff – including several who reported on sensitive subjects – were targeted with spyware which installed itself without the need to open or download any files.
An investigation by the Canada-based academic research unit Citizen Lab, prompted by Al Jazeera’s initial internal probe into the issue, discovered that the Israeli company Candiru was behind the attacks.
Analysts say the findings are “incredibly concerning”, as they confirm the existence of a new global security threat. “We knew we were headed in this direction and now it is out in the public,” Remesh Srinivasan, professor of information studies at the University of California in Los Angeles, US, told Al Jazeera.
“This is the next level, because people are being microtargeted,” he said. “This is the point we’ve come to when it comes to surveillance.”
How ‘zero-click’ malware works
Al Jazeera’s in-house technology team first discovered unusual patterns on devices used by some journalists in 2024. Analysis of network logs provided to the Citizen Lab by Al Jazeera in 2025 provided a clear temporal signature of how the attack was executed.
Malicious advertisements were bought by Discover-Tech, an Israeli company presenting itself as a legitimate advertising firm, but which actually operates as a facilitator for mercenary spyware partners.
Its advertisement network identified Al Jazeera staff, then quietly redirected them to an infected server belonging to Candiru. The spyware firm was blacklisted by the US government in 2021, when Citizen Lab found it was responsible for the illegal hacking and surveillance of at least 100 activists, journalists and political activists across 10 countries.
Al Jazeera Media Network has condemned the targeting of its staff members’ devices and called for those responsible to be held accountable.
Cybersecurity analyst and author Eddy Willems said the advertisements used automatically infect devices the moment they pop up on the screen, but there is an important technical nuance. “Executing code inside the browser does not automatically give an attacker full control over the computer,” Willems told Al Jazeera.
“To escape the browser’s isolated environment – the ‘sandbox’ – the attacker may need a second vulnerability,” Willems said, adding that an advanced spyware operation can combine several vulnerabilities.
“The attacker attempts to exploit vulnerabilities to bypass security boundaries. This is precisely what makes this type of attack so dangerous,” the analyst said.
Once the device is infected, the malicious software is designed to collect a wide range of sensitive data, including files, documents, and browser data such as cookies, bookmarks, and saved credentials.
It can also capture keystrokes, take screenshots, record microphone and webcam input, and extract emails and messages from popular communication platforms. To avoid triggering security mechanisms, the spyware often uses encrypted communication channels and breaks up stolen data into smaller chunks sent over time.
Advertising: A new global security threat?
Analysts say Citizen Lab’s findings point to the escalation of an existing threat, which expands the scale and reach of traditional cyberattacks and makes them much harder to detect.
While “zero-click” attacks are not completely new, the findings outline a new technique through which online advertisements are used as a route to infection.
Stephen O’Shaughnessy, a lecturer in cybersecurity at the TU Dublin Blanchardstown campus in Ireland, explained that when a user opens a website or app, an automated auction sells the advertisement space in a fraction of a second. That auction shares data about the victim, including the device ID, IP address, rough location and the app or site they are on.
“Discover-Tech posed as an ordinary advertiser, used that data to find their target and win the auction for that person’s screen,” O’Shaughnessy told Al Jazeera. “Anyone with a phone or browser that shows ads can be reached, without the attacker needing their phone number or email.”
“Because no message or link is involved, there is almost nothing for the victim to notice,” he added.
Discover-Tech appeared on lists of “certified” and “approved” vendors maintained by Google and advertising industry association IAB Europe, and has served advertisements via major networks such as Google, Yandex and Beeswax.
In its report, Citizen Lab said this illustrates the structural flaws in the online advertising system, which essentially failed to detect or prevent the abuse.
Discover-Tech advertisements have popped up on devices used by personnel in national-security-sensitive networks around the world, including those of various ministries of defence, armed forces, national cyber agencies, intergovernmental organisations and media outlets, Citizen Lab found.
The research unit said these advertisements have also appeared on networks used by the United Nations, NATO, the European Parliament, the European Commission and the Council of the European Union’s General Secretariat.
‘Almost nobody was watching’
Government networks have also been targeted in at least 24 countries, including the United States, Italy, Denmark, Norway, Australia, Russia, Mexico and Israel itself. Networks of media organisations have also been targeted, mainly in Australia, Denmark and Sweden, according to Citizen Lab.
In a separate report, New York-based advertising security firm Confiant said its own investigations had found that some of Discover-Tech’s advertisements also appeared in critical networks used by the Pentagon, the United Nations International Atomic Energy Agency and the International Criminal Court.
O’Shaughnessy said infection has not been confirmed there – only profiling of users. “But that alone is concerning, he said. “The ad system was built to send code from strangers to billions of screens with pinpoint targeting. Almost nobody was watching it from a security angle.”
The analyst said the risk remains low for most people as these attacks are expensive and aimed at specific targets. “For individuals at high risk, like journalists and officials, the best first defence is to install an ad blocker, switch off their advertising ID through their phone’s privacy settings, keep everything updated, and turn on Lockdown Mode or Android’s Advanced Protection,” he said.
Precautions also need to be taken within the industry and at government level. “To combat this, the ad industry needs to properly vet who’s buying ads,” O’Shaughnessy said, while “regulators need to stop personal data being sprayed out to thousands of unknown bidders in every auction.”
HM Passport Office has issued an urgent alert to UK passport holders
You’ll need a valid passport to travel internationally(Image: Lu ShaoJi via Getty Images)
HM Passport Office (HMPO) has issued an alert to all UK passport holders, urging some to act “as soon as possible”.
Anyone in the UK wishing to travel overseas requires a valid passport to do so, and applicants must hold British nationality to apply for or possess a British passport. That said, having British nationality does not automatically guarantee you a passport. You may not get a new one – or have an existing one confiscated – in a number of circumstances.
These include being under suspicion of a serious crime, being on bail, or having previously been repatriated to the UK at the government’s cost without repaying the sum. Many people may also be unaware that your passport never truly belongs to you – it remains government property and can be revoked or withdrawn at any point.
In a fresh warning on X, formerly Twitter, on Friday, HMPO shared some crucial advice for British passport holders. The post reads: “Lost your passport? Report it as soon as possible. Doing so helps protect against misuse and allows you to apply for a replacement.”
Additional guidance on GOV.UK clarifies that reporting your passport as lost or stolen straight away will “reduce the risk of anyone else using your passport or your identity”. You can report a lost or stolen passport on behalf of someone else if they’re unable to do it themselves.
How can I get a new passport quickly?
For those requiring a new or replacement passport as a matter of urgency, a one-day service is available, although “the earliest you can get an appointment is two days after you apply”. You will be required to surrender your old passport at your appointment.
Your new passport will be ready to collect from the passport office four hours after your appointment. Bear in mind this service is exclusively available for adult passport renewals, and carries a cost of £239.50.
Content cannot be displayed without consent
If you find yourself overseas and in urgent need of travel documents, you may be eligible to apply for an emergency travel document, though a fee will apply. Should you go down this route, there is no need to cancel your existing passport immediately, as it will be cancelled automatically as part of the emergency travel document application process.
BRITS could be in trouble if they plan jetting off for half-term as over 135,000 passports are set to expire before the end of the month.
This could wreak havoc for anyone heading away in October for a half-term break.
Hundreds of thousands of Brits have passports which will expire by the end of the yearCredit: AlamyWizz Air has found that over 135,006 passports are due to expire in OctoberCredit: ALBIT / SplashNews.com
Wizz Air has found that over 360,000 passports are set to expire before the end of the year.
The rule to remember is that British passports must have been issued within the last 10 years.
Lots of Brits fall victim of this rule as sometimes the expiry date can outdate the issue date.
For example, if a passport has July 2016 start date but a December 2026 expiry, it technically expired in July as it’s older than 10 years.
To travel to Europe and Schengen countries, passports must also be valid for at least three months after your planned return date.
Yvonne Moynihan, Managing Director at Wizz Air UK, said: “Nobody wants to arrive at the airport ready for their half term holiday only to discover there’s a problem with their passport.
“With more than 135,000 adult passports expiring this month alone, we’re encouraging anyone planning to travel to dig theirs out now and make sure everything is in order.”
Valid British passports cannot be older than 10 yearsCredit: Alamy
“Check your passport, check the entry requirements for where you’re going and get it sorted early if you need to.”
Yvonne added that if you’re heading on a Christmas getaway, it’s worth looking at your passport now so there’s time to renew it before December if you need to.